


The cryptocurrency landscape continues to face intense security scrutiny following a string of major incidents. An unidentified entity located within the European Union may have suffered a devastating financial blow, reportedly losing more than $106 million from accounts spread across multiple cryptocurrency exchanges. The massive security breach took place on Sunday, according to prominent on-chain investigator ZachXBT, sending fresh shockwaves through the digital asset community as investigators scramble to trace the pilfered funds.
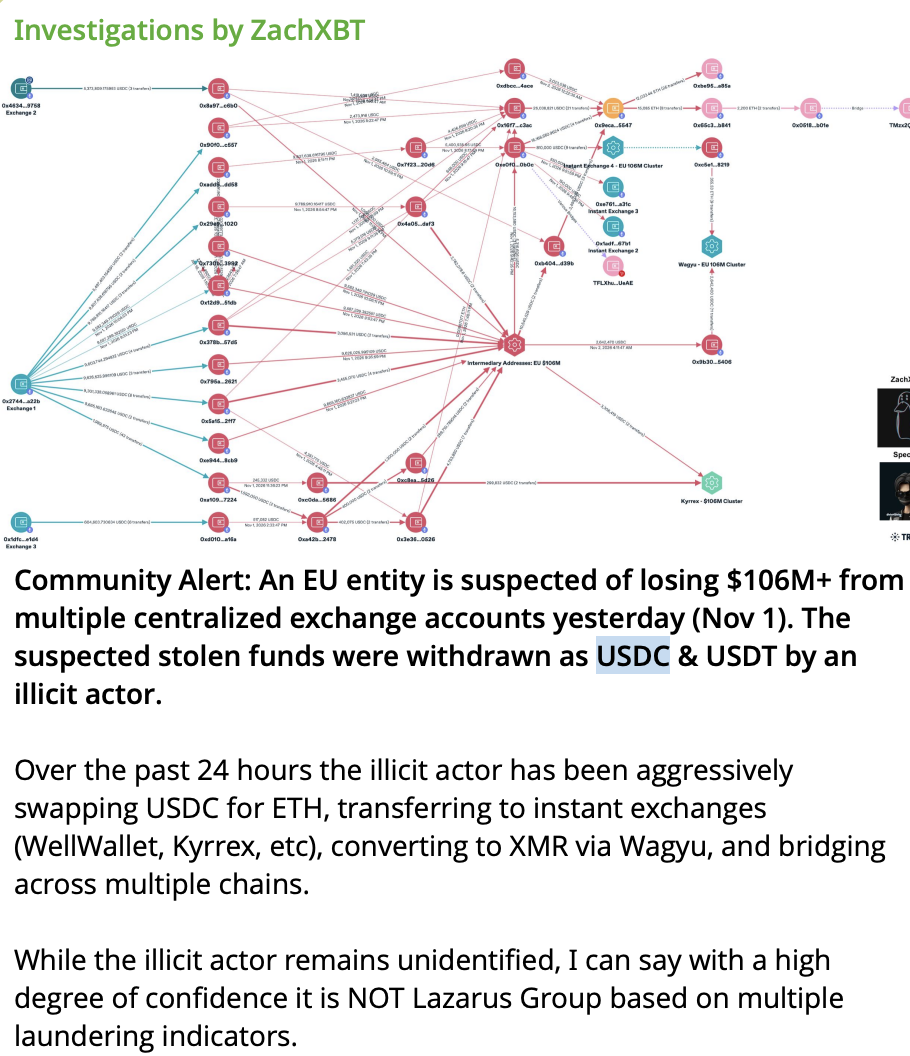
In a detailed update shared on Monday via his official Telegram channel, ZachXBT outlined the sophisticated methods used to siphon and launder the digital assets. According to the blockchain sleuth, the funds suspected of being stolen were initially drained and withdrawn in stablecoins, specifically USD Coin (USDC) and Tether (USDT). Once outside the primary exchange accounts, the perpetrator quickly initiated a complex laundering process designed to obscure the trail by moving the assets through a diverse array of cryptocurrencies and across multiple underlying blockchains.
The operational footprint left behind on the blockchain reveals a calculated strategy to evade tracking and law enforcement intervention. The suspected attacker swapped the stolen USDC holdings for Ether (ETH), utilizing various instant exchange services such as WellWallet and Kyrrex to facilitate the rapid conversion. Following these swaps, the funds were funneled through the swap service Wagyu and ultimately converted into Monero (XMR). Monero is a privacy-focused cryptocurrency renowned for its untraceable transactions, making it a frequent tool of choice for malicious actors seeking to sever the public link between stolen funds and their final destination.
Despite the intricate steps taken to mask the trail, ZachXBT noted that the tactical execution and movement patterns of the funds point away from any direct connection to North Korea’s infamous Lazarus Group or its associated fractions. At the time of reporting, the affected European entity has chosen to remain anonymous, and the specific centralized cryptocurrency exchanges targeted in the coordinated breach have not been publicly disclosed. To aid ongoing tracking efforts and community awareness, ZachXBT has successfully identified and flagged 11 specific wallet addresses directly associated with the movement of the stolen capital.
This substantial European exploit arrives on the heels of one of the darkest weeks in cryptocurrency security history. The industry is still reeling from the unprecedented $6.3 billion Binance hack that occurred on October 29. Federal law enforcement agencies, including the FBI, have officially attributed that record-breaking exploit to North Korean state-sponsored hackers known as "TraderTraitor," a cybercriminal collective operating under the broader umbrella of the Lazarus Group. The Binance incident stands as the single largest cryptocurrency theft on record, triggering massive capital flight and temporary withdrawal freezes as the exchange scrambled to stabilize its infrastructure and net outflows surged by billions of dollars.
Wallet Associated with Solana Arbitrage Bot May Have Lost $786K
While major industry players grapple with multi-billion-dollar state-sponsored heists, smaller-scale infrastructure targets continue to face severe threats. A cryptocurrency wallet associated with King, an automated trading bot operating on the Solana blockchain, may have fallen victim to a separate security compromise, resulting in an estimated loss of approximately $786,000 on Monday. The potential breach was first brought to light by pseudonymous blockchain monitoring and analytics account Onchain Lens.
King operates primarily as an arbitrage bot—a specialized automated software program designed to continuously scan different decentralized and centralized markets, instantly buying digital assets where they are priced lower and selling them where prices are higher to capture profit margins from market inefficiencies. Speaking to industry reporters, representatives from Onchain Lens detailed the suspicious transactional activity that triggered the alert. The funds in question were observed moving rapidly through a series of interconnected Solana wallets before being bridged over to the Ethereum network.
To execute this cross-chain transfer, the funds utilized Mayan, a specialized protocol designed for moving assets seamlessly between the Solana and Ethereum ecosystems. According to blockchain analysts, the high velocity of these transfers and the deliberate cross-chain routing are textbook indicators of an attacker attempting to obscure the origin of the funds, strongly implying that the underlying wallet infrastructure had been compromised by an unauthorized party.
Despite the compelling on-chain evidence and public disclosures by monitoring entities, the operator of the King trading bot has not yet issued an official statement confirming the security breach or confirming the loss of funds.
"Our report is based on unusual fund movements, rapid transfers, and the subsequent cross-chain movement of funds, which we believe indicates an attempt to obscure their origin," Onchain Lens explained in a statement. "This pattern strongly suggests a potential wallet compromise."

Comments (0)