


Federal Bureau of Investigation agents in Pennsylvania have arrested a senior executive from a Canadian cybersecurity firm in connection with an escalating international investigation into the notorious ShinyHunters hacking collective. The high-profile arrest follows a brazen cyberattack by the group that compromised sensitive personnel records of thousands of FBI agents, according to multiple sources familiar with the matter.
The New York Times reported that federal authorities apprehended the Canadian man in Pennsylvania on suspicion of providing assistance to ShinyHunters. While neither the initial newspaper report nor a public statement published on social media platform X by FBI Director Kash Patel explicitly named the individual, a sequence of court documents and insider accounts have helped piece together the contours of the unfolding federal case.
According to a source close to the active investigation, the visiting Canadian executive was in Pennsylvania to attend a prominent cyber insurance conference. The suspect’s professional background centered heavily on handling high-stakes ransomware negotiations and extortion advisories on behalf of corporate clients targeted by cybercrime syndicates. Another source noted that oversight and control of the broader ShinyHunters investigation have recently been centralized at a primary FBI field office in Texas.
Digital footprints left across online event schedules indicate that the annual Cyber Risk Summit was hosted at the Loews Philadelphia Hotel between October 5 and October 7. While the conference drew sponsorship from various tech and insurance entities, event documentation reveals that the summit’s single largest corporate sponsor was a Canadian cybersecurity firm operating under the name Cypfer.
Public professional networking profiles on LinkedIn indicate that an individual named Edward Dubrovsky was previously identified as a co-founder of Cypfer before transitioning to another Canadian security company and conference sponsor known as CyberSteward. Approximately one month prior to his apprehension, Dubrovsky published a post on LinkedIn announcing his travel plans to attend the Philadelphia Cyber Risk Summit alongside colleagues from the CyberSteward team.

Following initial inquiries, a spokesperson for Cypfer clarified that Dubrovsky was never a founder or co-founder of the organization, as his online biography had asserted, but instead served as a managing director prior to his resignation in December 2025.
Dubrovsky had previously promoted his professional trajectory online, writing in a social media post that he looked forward to continuing strategic discussions regarding compliance-driven, coercive extortion advisory services, ransomware negotiations, and cross-border settlement solutions that remain globally agnostic.
Federal court records retrieved from the Eastern District of Pennsylvania indicate that an individual named Edward Dobrovsky—reflecting a minor spelling variation in the surname—was formally arrested on October 8, facing preliminary charges of cyber extortion and conspiracy. A significant portion of the evidentiary documentation, including the primary criminal complaint, remains legally sealed under court order. However, select filings indexed by legal tracking platforms outline specific criminal counts, charging the defendant with conspiracy to threaten the impairment of information confidentiality with the intent to exact financial ransom, alongside interference with commerce by means of threats.
U.S. Bureau of Prisons inmate location records confirm that a 54-year-old Edward Dubrovsky is currently detained at a federal holding facility located in Philadelphia. Nonetheless, court docket entries show that a transfer notice was filed on October 9 moving the proceedings to the Eastern District of Texas, which sources describe as the central hub for the government’s comprehensive ShinyHunters probe. The FBI has officially declined to comment on the ongoing legal proceedings.
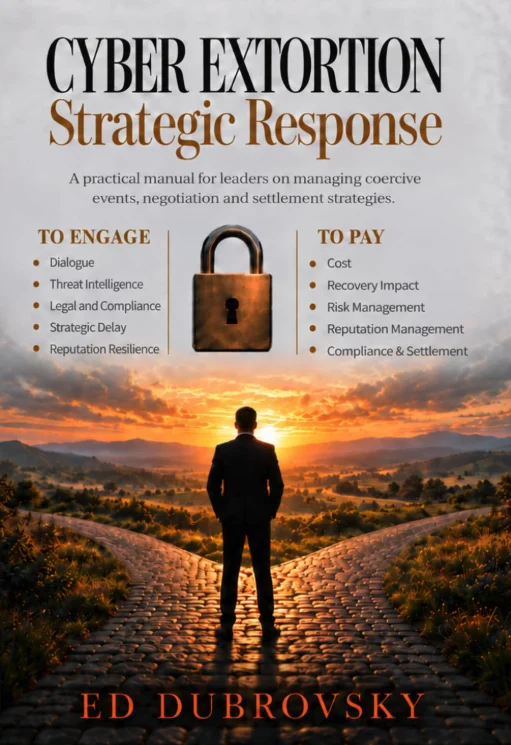
Beyond his executive roles in corporate cybersecurity, Dubrovsky is the author of a published 252-page volume titled Cyber Extortion Strategic Response. Promotional materials for the book state that it aims to guide readers past the initial shock of a ransom demand and into the complex decision-making processes required for corporate incident response, operational recovery, and asset protection.
An excerpt from the book’s publisher summary underscores a distinct philosophy regarding digital extortion: communicating with a malicious cyber actor is not equivalent to negotiating a financial payout, and entering into dialogue does not constitute an explicit commitment to pay. According to the text, communication can fulfill alternative strategic objectives, such as validating threat actor claims, collecting valuable intelligence, buying critical operational time, and preserving institutional options while leadership evaluates subsequent courses of action.

Legal representatives for Dubrovsky could not be reached immediately for comment, and attempts by reporters to contact other executives at CyberSteward yielded no immediate response. Available court docket sheets reflect that the defendant has not yet retained private legal counsel, nor has the court formally appointed a public defender to represent him.
The ShinyHunters syndicate has established a reputation within the global cybersecurity community for executing targeted phishing campaigns and leveraging stolen credentials to infiltrate corporate software-as-a-service environments. Once inside, the group typically exfiltrates proprietary data and threatens to leak the sensitive material publicly unless an extortion demand is satisfied. Federal law enforcement estimates indicate that the collective has successfully extorted upward of $70 million from corporate and organizational victims during the current calendar year alone.
Investigators have spent weeks sifting through digital media and hardware devices seized last month during an operation in the Netherlands, where local police apprehended reformed hacker Pepijn van der Stap in connection with the same multi-jurisdictional ShinyHunters investigation. Sources familiar with the inquiry suggest that additional criminal charges against principals at other firms specializing in ransomware mediation and negotiation may be forthcoming as the dragnet widens.
The pressure surrounding the case escalated dramatically immediately following Van der Stap’s arrest, when another prominent figure within the ShinyHunters network, operating under the alias "Rey," assumed operational command of the group. The newly empowered leader launched public taunts directed at the FBI regarding a high-profile breach of the agency’s online recruitment portal. That specific intrusion exposed sensitive personnel details, including individual unit assignments, professional specializations, and confidential medical and psychiatric records.
Law enforcement efforts soon closed in on the digital network. Investigative reporting revealed that the individual operating as Rey was identified as a teenager named Saif Al-din Khader. Authorities detained the young hacker, who subsequently began cooperating with federal investigators. Court and reporting details noted that Khader was apprehended just as the cybercrime unit allegedly attempted to execute an extortion scheme against a digital aviation and navigation unit recently divested by aerospace giant Boeing.
As federal authorities continue to execute search warrants, analyze seized digital infrastructure, and unravel the network’s commercial intermediaries, the federal investigation into ShinyHunters and its ecosystem remains fluid.

Comments (0)