


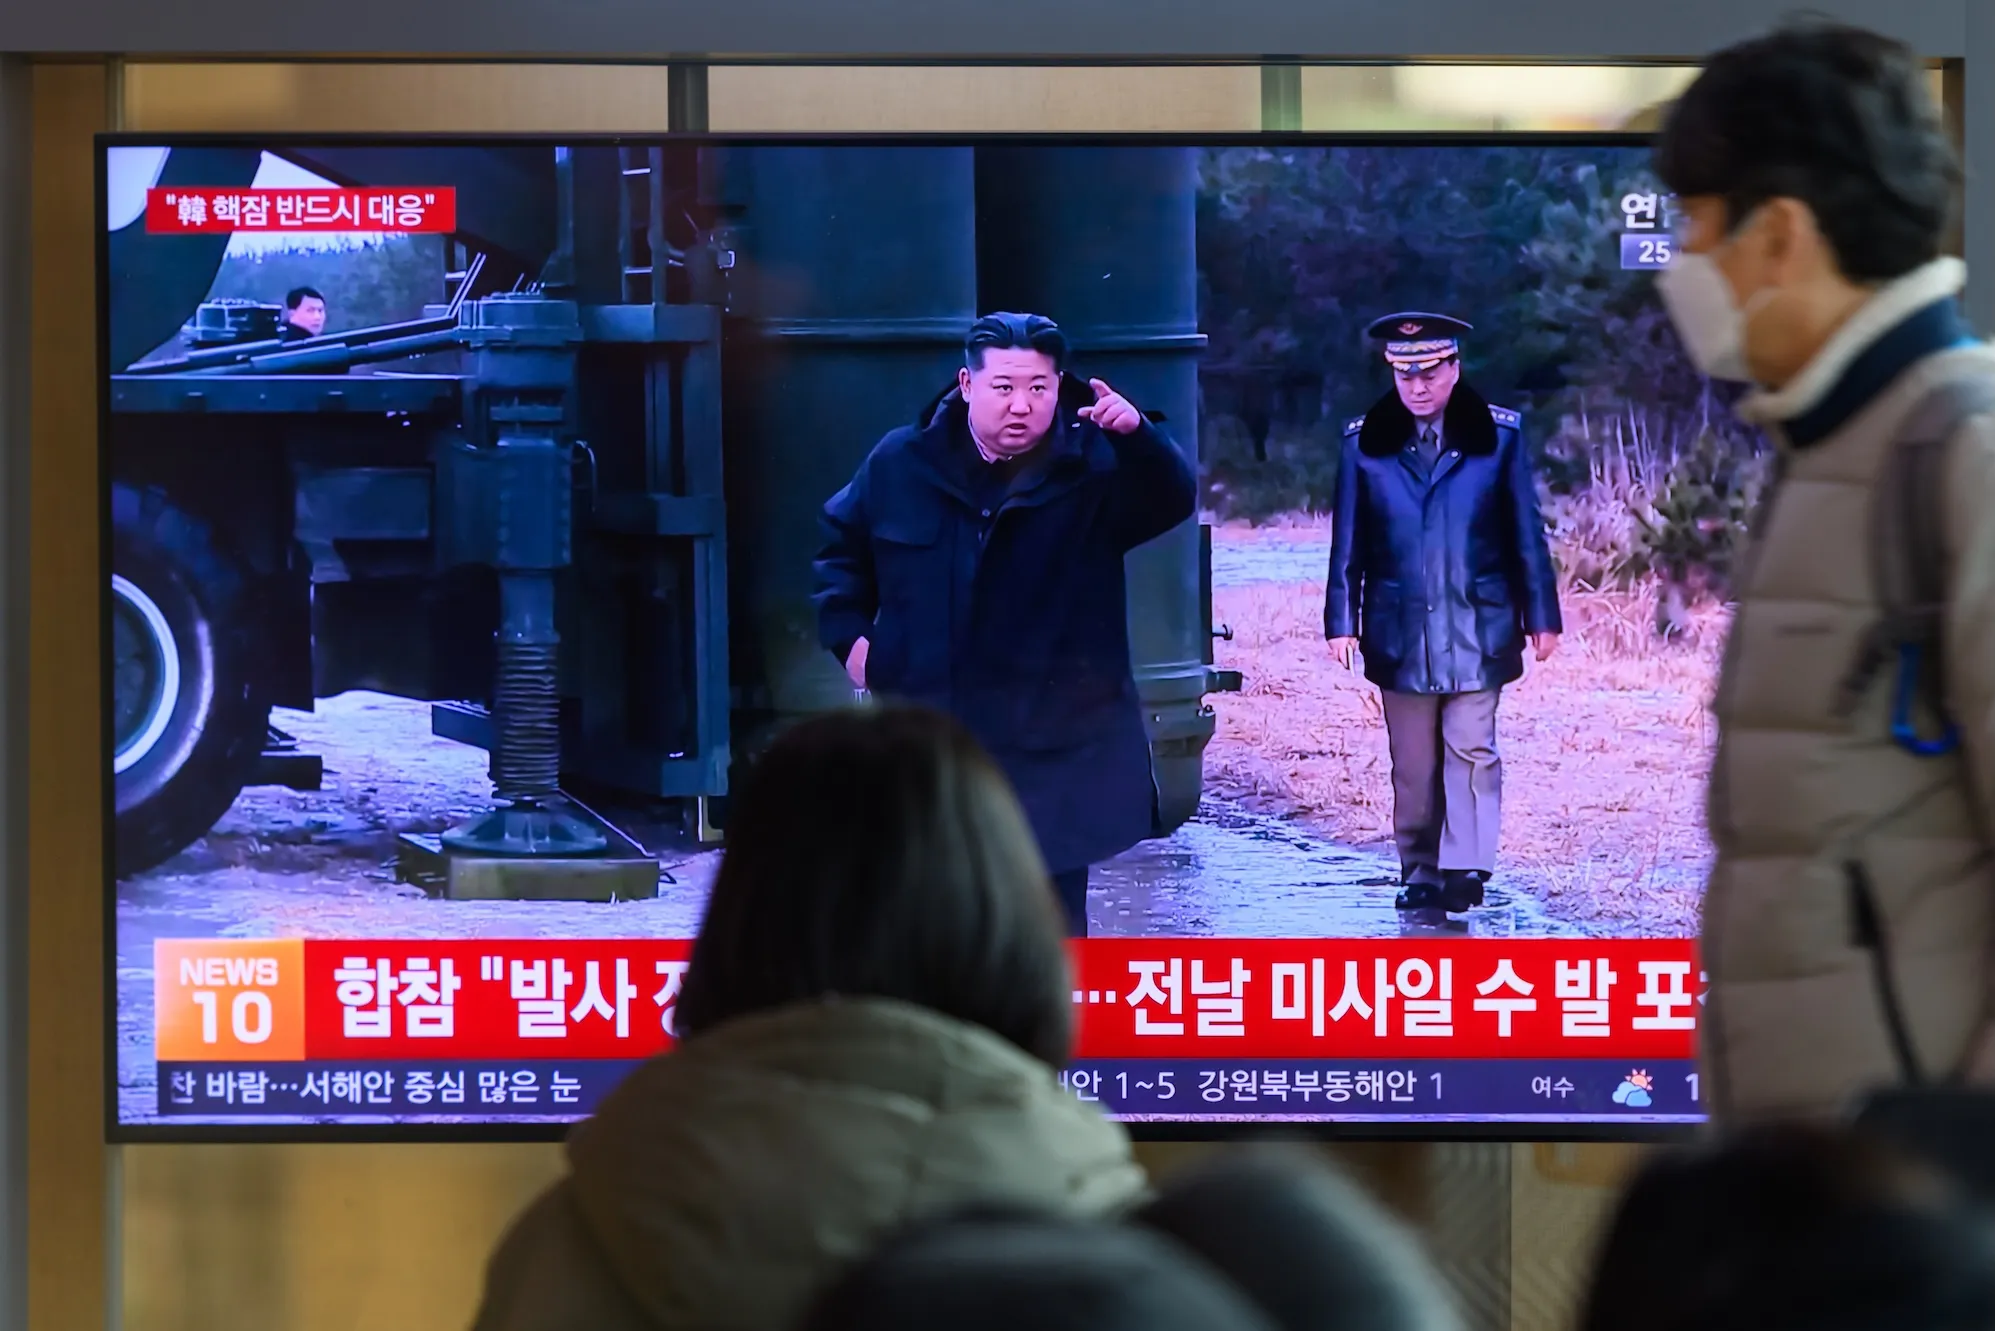
Cryptocurrency giant Binance has confirmed that state-sponsored hackers from North Korea used an elaborate, months-long social engineering campaign—featuring fake social media profiles and a fictitious job offer—to trick an employee into downloading malicious software, laying the groundwork for the theft of a record $6.3 billion in digital assets.
The massive breach, which was disclosed in an updated statement posted on X, forced the world’s largest cryptocurrency exchange to temporarily suspend customer withdrawals across its network. The heist has sent shockwaves through the global financial and tech sectors, drawing immediate scrutiny from federal law enforcement and blockchain security analysts.
According to the Federal Bureau of Investigation and independent blockchain investigators, North Korea is directly responsible for the staggering cyberattack. The isolated nation has long been accused by international governments of orchestrating massive cryptocurrency thefts to fund its internationally sanctioned nuclear weapons program, relying heavily on cyber operations to bypass global financial restrictions.
The Anatomy of a Sophisticated Phishing Scheme
In its detailed statement, Binance shed light on the initial vector of the compromise. North Korean hackers, operating behind meticulously crafted fake personas posing as corporate recruiters, established contact with a software engineer responsible for managing wallet infrastructure at the company.
The interaction appeared entirely professional. After conducting two formal interviews with the purported recruiters, the targeted employee was instructed to download an apparent coding assignment as part of the standard interview evaluation process. Unbeknownst to the engineer, opening the assignment executed malicious code designed to compromise their work-issued laptop. Binance acknowledged that its internal endpoint security tools failed to detect the advanced malware at the time.
This initial foothold gave the attackers the leverage they needed to move laterally within Binance’s internal network. Armed with access to the first engineer’s machine, the hackers reached an internal administrative tool capable of compromising the work computers of two additional engineers on the wallet team.
The escalation pathway revealed further vulnerabilities in operational security. One of the subsequent victimized engineers had unwittingly downloaded a tampered application containing password-stealing malware months earlier, having encountered the malicious software through ordinary search engine results. Although Binance had previously replaced that engineer’s compromised laptop, the hackers managed to leverage previously stolen credentials from that machine to breach the computer of a third engineer. This final target possessed system privileges that granted direct control over critical infrastructure handling billions of dollars in cryptocurrency.
Reflecting on the scale of the breach, Binance stated that the successful intrusion "should not have happened." The company reported that it has since taken aggressive steps to overhaul its network security architecture to prevent similar vectors of compromise.
A Persistent Threat to the Tech and Crypto Sectors
The catastrophic heist highlights an increasingly prevalent tactic within North Korea’s advanced persistent threat playbook, which increasingly targets cryptocurrency exchanges, decentralized finance platforms, and high-net-worth individuals. For years, cybersecurity researchers have warned that state-backed operatives frequently pose as venture capitalists, startup investors, and recruiters. Using comprehensive dossiers of stolen Western identities, these actors build long-term rapport with target employees before deploying malicious payloads.
These social engineering schemes are widely known across the digital asset industry and have been the subject of repeated, urgent warnings from the U.S. government and major cybersecurity firms. Data from threat intelligence providers indicates that North Korean operatives disguised as remote IT workers and fake corporate recruiters were behind roughly half of all successful network intrusions at U.S. technology companies over the prior year.
By Binance’s own internal accounting, the platform faced at least 57 suspected attack attempts originating from North Korean actors leading up to the breach. The exchange noted that these figures reflect the relentless and persistent threat posed by state-sponsored cyber espionage units targeting the cryptocurrency sector.
However, the question of how the hackers successfully convinced a high-level engineer to execute unauthorized software—despite widespread industry warnings—and how they bypassed deeper security barriers within Binance’s corporate network remains a central focus for investigators.
While the incident exposes the sheer effectiveness of modern social engineering tactics such as fraudulent employment offers, cybersecurity experts emphasize that enterprises carry the ultimate responsibility for ensuring their infrastructure cannot execute unauthorized or untrusted software capable of initiating a systemic compromise.
Questions Surrounding Internal Defenses
When contacted for comment, Binance spokesperson Ross O’Leary pointed to the company’s official public statements but declined to answer specific, on-the-record questions regarding the incident from reporters. Unanswered inquiries included details on how Binance prevents unauthorized or malicious code from executing on employee workstations, and whether independent third-party cybersecurity audits of the company’s network had been conducted prior to the multi-billion-dollar breach.
In the wake of the disaster, Binance announced that it is bringing in external cybersecurity specialists to conduct a comprehensive forensic review of the attack. The exchange has also implemented stringent new security protocols across its enterprise environment to safeguard against future threats.
Despite these remedial measures, the incident stands firmly in the history books as the largest single cryptocurrency theft ever recorded.

Comments (0)