


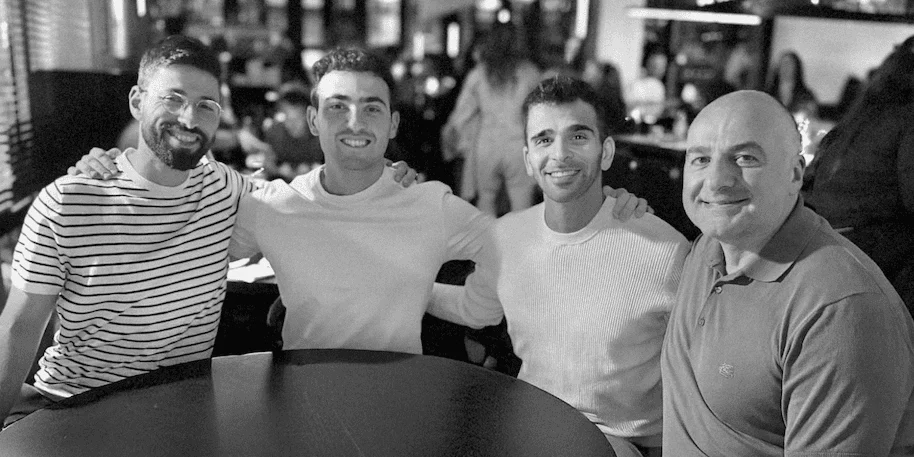
When venture capitalists first met Yair Saban and Niv Hoffman, the founders did not yet have a company, a corporate name, or a commercial product. What they did possess, however, was an undeniable reputation forged within the elite ranks of the Israeli cybersecurity ecosystem. As early-stage investors ran background checks and reference calls across the tight-knit Israeli tech community, a consistent narrative quickly emerged: Saban and Hoffman were widely regarded as being among the absolute strongest prospective founding teams in the country.
One former commander of Unit 8200, the legendary technological intelligence agency of the Israel Defense Forces, offered a particularly striking endorsement, noting that Saban was the only person the commander had ever encountered who possessed every single requisite trait to one day command Unit 8200 itself. Meanwhile, Hoffman was recognized across the industry as a technical outlier who previously spearheaded the unit’s most critical vulnerability research department while cultivating a formidable network of elite engineering talent. The velocity at which the founders operate became immediately clear when Saban completed his military service on a Thursday, and the investors shook hands on a seed-stage financial commitment just two days later on Saturday.
Before turning their attention toward building commercial defensive security software, the duo demonstrated their formidable offensive capabilities by creating MOAK, colloquially dubbed the "Mother of All KEVs." MOAK is an advanced agentic workflow designed to autonomously generate working exploits for freshly published software vulnerabilities without requiring any human intervention. To illustrate the terrifying speed at which automated threats operate, the founders demonstrated MOAK exploiting a critical React vulnerability in a mere 21 minutes—a stark contrast to the estimated six days typically required for an enterprise organization to develop, test, and deploy a standard software patch. They publicly released the project to sound a serious alarm bell across the technology sector, warning that the industry was severely underestimating the massive leverage malicious actors could rapidly gain through artificial intelligence, and insisting that defensive tooling urgently needed to evolve to meet the challenge.
The inherent architectural vulnerability of modern software began the day developers shifted from writing custom code from scratch to importing third-party packages built by external parties, effectively establishing a complex software supply chain. It subsequently took the technology industry two decades and a string of painful, high-profile security incidents—ranging from the widespread Log4j vulnerabilities to the sophisticated SolarWinds supply chain breach—to construct the necessary operational machinery required to inspect and secure incoming software components.
Artificial intelligence agents now face an identical structural crisis, with one critical distinction: an agent’s supply chain is assembled dynamically at runtime, and in many enterprise environments, absolutely nobody is inspecting it. Modern enterprise agents continuously consume an array of external capabilities, including specialized skills, third-party plugins, Model Context Protocol (MCP) servers, sub-agents, custom hooks, operational commands, and behavioral rules. Each of these components typically executes with the agent’s full permissions, operating directly inside the user’s local environment and accessing sensitive user data. Alarmingly, these potentially dangerous extensions are frequently installed with the casual carelessness that most people reserve for downloading a random browser extension.
Over the past several months, Air has systematically demonstrated the immense stakes involved in this emerging threat landscape. The startup’s researchers engineered a deliberately malicious skill and watched as multiple prominent AI marketplaces routinely waved it through, approving the hazardous code as safe. Their published research initiative, titled "The Story of Skills," revealed that a researcher-built malicious skill successfully reached more than 26,000 active agents through trusted distribution marketplaces and social media channels, effortlessly bypassing every commercial security scanner along the way.
In a subsequent research disclosure known as "SkillJacking," the company exposed that 925 live, publicly available skills were improperly pulling their critical dependencies and underlying prompts from dead or abandoned web links. Air strategically registered those abandoned links and instantly assumed complete control over the approximately 134,000 corporate and individual agents that had previously installed the compromised skills, proving once again that public security scanners completely missed the underlying architecture flaws.
Demonstrating the rapid execution pace that initially caught the attention of investors, Saban and Hoffman released ScanAir on the exact same day as their research disclosures. ScanAir is an OWASP-aligned security scanner specifically tailored for agentic skills and add-ons. This repeating operational sequence—discovering a critical security hole, empirically proving its exploitability, publishing the findings transparently, and immediately shipping the defensive tooling required to close the gap—represents the core philosophy of the founding team.
Today, Air offers a comprehensive suite of three distinct products designed to cover the entire lifecycle of an artificial intelligence agent’s add-ons and extensions. The first product, Air Filter, vets every single prospective add-on before an agent is ever permitted to consume it, utilizing a combination of rigorous static analysis, dependency verification, and automated sandbox detonation. It then intercepts unsafe installations in real time and intelligently offers secure alternatives in their place.
The second product, Air Defend, continuously monitors what agents are actually executing once they are actively running in production, providing enterprise security operations teams with advanced detection and incident response capabilities for erratic or malicious agent behavior. Finally, Air Control manages organizational security posture and governance policies, providing visibility into which agents currently exist, what system resources they are permitted to access, and the ability to instantly revoke a compromised skill across thousands of deployed agents simultaneously.
Industry observers have likened this multi-layered architecture to a comprehensive residential security system: Air Filter acts as the secure deadbolts and childproofing measures on the doors, Air Defend functions as the security cameras and the vigilant guard monitoring the feeds, and Air Control serves as the master control panel by the front door where every entry point is accounted for, every access code is assigned, and all permissions can be revoked at a moment’s notice.
Throughout the evolution of the Israeli technology sector, every few years sees the emergence of a new generation of elite cyber talent coming out of Unit 8200 and consolidating around a select group of high-potential startups. The wave that brought forth companies like Wiz, Cyera, and Island was followed by Eon, Glow, Decart, and Kela, and the current landscape is now unmistakably anchored by Air. Saban and Hoffman have demonstrated themselves to be exceptionally sharp, driven natural leaders with a proven ability to attract extreme talent density, successfully assembling a world-class team of top-tier engineers in a remarkably short span of time. Building upon the initial seed investment led by Sequoia Capital, the venture firm is now doubling down on its partnership by leading Air’s Series A funding round.
As enterprise organizations increasingly move toward granting artificial intelligence agents genuine autonomy and real authority over critical business systems, chief information security officers everywhere will inevitably be forced to answer difficult questions regarding their operational security. Leadership will need to definitively explain precisely what code their agents are running, where those software components originated, and who verified their safety. While few organizations currently possess complete answers to these pressing questions, Air is rapidly constructing the definitive system of record designed to solve the agent supply chain crisis.

Comments (0)