


Federal Bureau of Investigation agents have arrested a high-profile executive from a Canadian cybersecurity firm in Pennsylvania, marking a dramatic escalation in a federal investigation into the notorious ShinyHunters hacking collective. The arrest follows a brazen cyberattack attributed to the group that compromised sensitive personnel records of thousands of FBI agents.
According to multiple sources close to the investigation, the detained individual was in Pennsylvania to attend a prominent cyber insurance conference. The suspect’s professional background is deeply intertwined with the specialized industry of handling ransomware negotiations and cyber extortion advisory services on behalf of corporate clients navigating high-stakes digital security crises.
The New York Times first reported the apprehension of the Canadian man on suspicion of aiding the ShinyHunters operation. While neither the Times nor a public statement published on social media by FBI Director Kash Patel initially identified the suspect by name, federal court records and industry sources quickly illuminated the details surrounding the enforcement action.
Sources familiar with the matter revealed that the suspect was visiting Philadelphia for the annual Cyber Risk Summit, a major industry gathering held at the Loews Philadelphia Hotel. Conference documentation and online archives indicate that the summit’s primary corporate sponsor was a prominent Canadian security firm called Cypfer.

Public professional profiles and industry databases connect the detained executive to the upper echelons of the Canadian cybersecurity sector. Cypfer representatives clarified that the individual previously served as a managing director at the firm before resigning in late 2025, rather than functioning as a co-founder as indicated on social media platforms. Following his departure from Cypfer, the executive became associated with CyberSteward, another Canadian security firm and conference sponsor, expressing enthusiasm on professional networks about continuing specialized work in global ransomware advisory and settlement negotiations.
Federal court filings show that an individual matching the suspect’s identity and professional background was arrested in Pennsylvania on October 8, facing charges related to cyber extortion and conspiracy. While several core investigative documents, including the primary criminal complaint, remain sealed from public view, dockets indexed at CourtListener.com shed light on the nature of the allegations. The defendant is charged with conspiracy to threaten to impair the confidentiality of information with the intent to extort money, alongside charges of interference with commerce by threats.
U.S. Bureau of Prisons records initially placed the 54-year-old executive at a federal detention facility in Philadelphia. However, subsequent legal notices filed on October 9 indicate that the jurisdiction of the case has been transferred to the Eastern District of Texas. Sources indicate that the FBI field office in Texas has become the centralized nerve center for the sprawling, multi-jurisdictional investigation into the ShinyHunters syndicate. The FBI has consistently declined to comment on the ongoing proceedings.
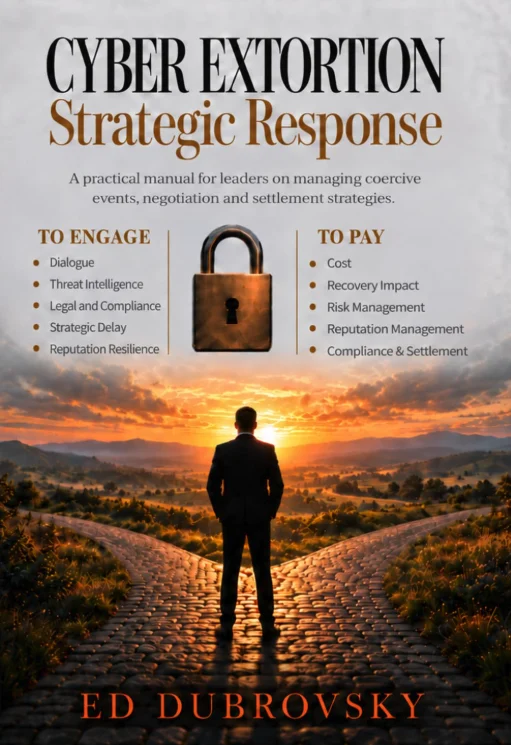
The arrested executive is also a recognized author within the cybersecurity community, having penned a book dedicated to the complex operational strategies of responding to cyber extortion. The text focuses heavily on the delicate mechanics of communicating with malicious actors, emphasizing that dialogue with cybercriminals does not inherently constitute a commitment to pay ransoms, but can instead serve as a tactic to gather intelligence, test threat actors’ claims, and buy critical time for victimized organizations. Court records indicate that the defendant has not yet retained private counsel or had a public defender formally appointed by the court.
The arrest occurs against the backdrop of a relentless campaign by ShinyHunters, a cybercrime faction known for leveraging sophisticated phishing techniques and stolen credentials to siphon proprietary data from corporate software-as-a-service providers. The group typically pressures organizations by threatening to leak sensitive corporate repositories online unless substantial extortion demands are met. According to federal estimates, the syndicate has successfully extracted more than $70 million from various corporate and institutional victims throughout the year.

Law enforcement pressure on the collective has intensified significantly in recent weeks. Investigators have been meticulously analyzing digital devices seized during a late-September operation by Dutch law authorities, who apprehended reformed cybercriminal Pepijn van der Stap in connection with the ShinyHunters network. Sources suggest that the ongoing scrutiny could soon yield additional criminal charges against principals at other specialized ransomware negotiation firms.
The pressure on the hacker collective also triggered erratic and brazen retaliation. Immediately following Van der Stap’s detention, an operative operating under the alias "Rey" assumed control of the ShinyHunters organization and began aggressively taunting federal authorities. The threat actor publicly circulated stolen data extracted from an online recruitment portal utilized by the FBI, which included detailed records concerning agents’ unit assignments, professional specializations, and confidential medical and psychiatric evaluations.
Subsequent international reporting revealed that the individual operating behind the alias "Rey" was a teenager named Saif Al-din Khader. Authorities successfully detained Khader, who has since begun cooperating with federal investigators. The apprehension coincided with the group’s attempts to mount an extortion campaign against a digital aviation and navigation unit recently divested by Boeing.
As federal authorities continue to untangle the web of international cybercrime and third-party facilitation, the case remains subject to rapid developments.

Comments (0)