


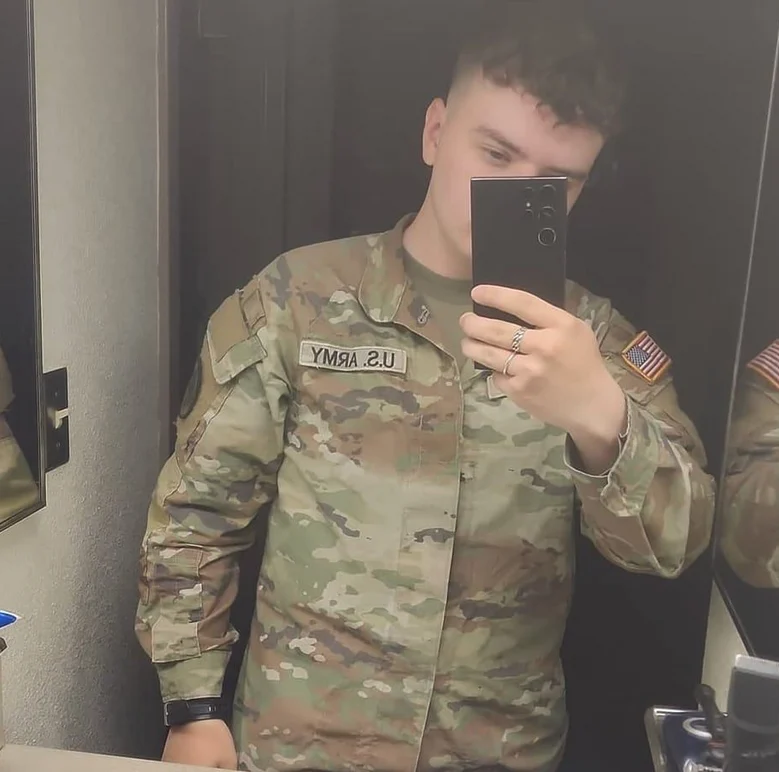
A U.S. Army soldier who pleaded guilty to hacking into multiple telecommunications companies and stealing mobile call and text metadata belonging to more than 100 million AT&T customers was sentenced to 70 months in federal prison today in Seattle. In addition to the prison term, the defendant was ordered to pay nearly $300,000 in restitution to his victims, bringing a significant chapter to a high-profile international cybercrime investigation that exposed profound vulnerabilities in cloud data storage and corporate cybersecurity practices.
Cameron John Wagenius, a 22-year-old soldier who was stationed at a U.S. Army base in South Korea at the time of the offenses, operated under the online cybercriminal persona “Kiberphant0m.” Working alongside a network of alleged co-conspirators, Wagenius exploited a major vector affecting cloud data storage provider Snowflake. By leveraging exposed credentials on accounts that failed to enforce multi-factor authentication—a security gap that has since prompted Snowflake to mandate multi-factor authentication across all accounts—the group managed to download vast troves of sensitive data from several large enterprise customers.
The scope of the breaches came to light in October 2024, when Wagenius took to cybercrime forums to publicly brag about his exploits. He claimed to have successfully stolen call and text metadata, including source and destination numbers, timestamps, and call durations, for tens of millions of AT&T customers. Furthermore, Kiberphant0m boasted about hacking into more than a dozen telecommunications companies worldwide, including Verizon’s Push-to-Talk business, and resorted to public extortion tactics, threatening to publish the stolen records unless the affected corporations met his demands.
The trail leading to his capture began to form in late November 2024, when security journalism outlet KrebsOnSecurity published findings indicating that the individual operating as Kiberphant0m was likely a U.S. soldier stationed in South Korea. Less than a month after those reports surfaced, Wagenius was apprehended and subsequently faced two separate federal indictments. Demonstrating cooperation with federal authorities following his arrest, Wagenius quickly pleaded guilty to all counts across both cases.
During his sentencing hearing in Seattle, federal judges formally handed down the nearly six-year federal prison sentence, alongside an order for $294,978 in restitution. Federal prosecutors outlined a broader criminal enterprise, noting that Wagenius was assisted in his extortion campaigns by Kenneth Schuchman, a 28-year-old resident of Vancouver, Washington, who possesses a documented and extensive history in the cybercrime underground. Schuchman’s criminal record includes a 2019 guilty plea for operating the Satori botnet, a vast network of compromised Internet-of-Things devices utilized to orchestrate large-scale distributed denial-of-service attacks.
Wagenius’s other alleged co-conspirators are facing separate legal proceedings for their roles in the Snowflake data thefts. Conor Riley Moucka, operating under the alias “Judische” in Kitchener, Ontario, was arrested in 2024 and entered a guilty plea in August 2026. Meanwhile, John Erin Binns, an American citizen currently residing in Turkey, remains wanted by law enforcement for his alleged involvement in a massive 2021 data breach at T-Mobile that compromised the personal information of at least 76 million customers.
As the extortion scheme unraveled, Kiberphant0m’s tactics escalated to include the re-extortion of victim companies and even threats to disclose sensitive national security secrets. Following the arrest of Moucka—and despite the fact that AT&T had already paid the extortion ring a ransom of $370,000 in Bitcoin—Kiberphant0m retaliated by publishing files on hacker forums. He claimed these files included AT&T call logs belonging to then President-elect Donald Trump and then Vice President Kamala Harris, alongside technical schematics allegedly stolen from the U.S. National Security Agency.
The multi-agency pursuit of Wagenius highlights the unique challenges law enforcement faces when military insiders turn to cybercrime. Paul Russell, a resident agent in charge at the Defense Criminal Investigative Service, the criminal investigative arm of the U.S. Department of Defense Office of Inspector General, detailed the urgency of the investigation once military ties were established. Upon receiving intelligence that an active-duty soldier holding a secret security clearance was actively developing hacking tools and trafficking in stolen data, DCIS joined forces with the Federal Bureau of Investigation, the Army Criminal Investigative Division, and the U.S. Secret Service.
According to Russell, discovering an insider threat of this magnitude was an extraordinary occurrence that immediately mobilized federal partner organizations. Investigators acknowledged that the convergence of active military service, a security clearance, and international extortion made the case exceptionally dangerous and unpredictable from the very beginning.
Compounding the severity of his initial crimes, a sentencing memo filed by federal prosecutors in Seattle revealed that Wagenius continued his illicit technological explorations even while incarcerated and awaiting sentencing. The government’s memo documented that Wagenius repeatedly violated the computer use policies of the Bureau of Prisons in an effort to probe the vulnerabilities of BOP internal computer systems.
Records cited by prosecutors showed that around September 2025, Wagenius utilized another inmate’s email system to instruct the recipient to prompt a commercial artificial intelligence tool for technical data regarding privilege escalation and bypass vulnerabilities in Windows 10 Enterprise, explicitly asking for real-world working scripts without omitted code. Less than a week later, utilizing a different inmate’s account, he requested step-by-step exploitation details and code for CVE-2023-45208, a command injection vulnerability affecting D-Link networking devices. During the same period, he also sought instructions on constructing improvised antennas within a prison environment using commissary items to extend radio reception, alongside inquiries concerning prison escape methods.
Prosecutors noted that Wagenius frequently framed these artificial intelligence queries as research for a book he claimed to be writing. Authorities pointed to this method as a classic example of prompt injection, where attackers craft deceptive inputs to bypass the safety guardrails programmed into commercial AI tools to prevent the generation of malicious exploit code. While the government found no evidence that Wagenius successfully deployed these researched vulnerabilities against BOP networks—with the defendant claiming he was merely researching potential weaknesses to inform the bureau—the activity underscored a persistent intent to manipulate technology.
Despite the massive scale of the data he accessed and the immense market value of the stolen corporate records, Wagenius’s criminal enterprise yielded surprisingly low financial rewards. According to the government’s sentencing memo, Wagenius ultimately generated a meager total of approximately $1,500 from selling the stolen data.
Federal prosecutors summarized the dichotomy of his criminal career in the sentencing memorandum, noting that while Wagenius was ultimately unsuccessful as a profitable cybercriminal, his actions caused deliberate, widespread, and significant harm to individual victims, major U.S. corporations, and the national government.

Comments (0)