


A teenager from Amman, Jordan, suspected of acting as a key leader for the prolific data theft and extortion syndicate known as ShinyHunters, has been detained by local authorities and is reportedly cooperating with the FBI to identify other members of the hacking collective.
According to intelligence gathered by KrebsOnSecurity, the suspect—who operates online under the hacker handle “Rey”—was apprehended just as the group was in the midst of extorting a business unit recently divested by the global aerospace giant Boeing. Notably, Boeing manufactures the aircraft fleet utilized by Royal Jordanian Airlines, the employer of Rey’s father.
The Arrest and Identification of "Rey"
On October 3, Reuters cited three unnamed sources confirming that a suspected ShinyHunters member in Amman, identified as Saif Al-din Khader, had been detained by Jordanian law enforcement and was actively cooperating with federal U.S. investigators. KrebsOnSecurity previously unmasked Rey as Khader in a November 2025 investigative profile, wherein the young man admitted to working alongside multiple ransomware factions.
Rey re-entered the global spotlight following an exclusive report on the Dutch police’s arrest of 24-year-old convicted cybercriminal Pepijn van der Stap. Van der Stap was apprehended on suspicion of facilitating data thefts and extortion schemes on behalf of ShinyHunters. Investigators noted that immediately following the Dutchman’s arrest on the evening of September 15, Rey assumed control over the ShinyHunters brand. He quickly began boasting publicly about stealing highly sensitive data from the FBI and extorting the rival ransomware group Cl0p.
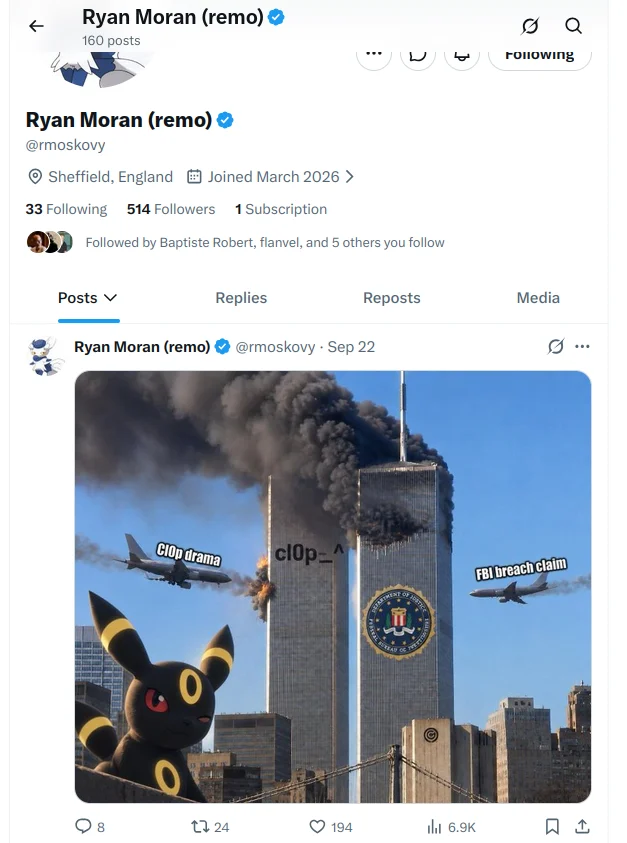
Using his long-standing account on Twitter/X, Rey taunted both the FBI and Cl0p with custom memes. At the same time, he embedded images of the avatar utilized by Van der Stap’s former hacker alias, “Umbreon,” in what appeared to be a calculated attempt to frame the Dutch national for the high-profile breaches.
The Oracle PeopleSoft Exploit and FBI Breach
As detailed in previous cybersecurity advisories, ShinyHunters infiltrated the FBI’s recruitment portal and other corporate networks by exploiting a critical zero-day vulnerability, cataloged as CVE-2026-35273, within Oracle’s PeopleSoft software-as-a-service (SaaS) platform. PeopleSoft is widely deployed across industries for managing human resources, payroll, recruitment, and employee benefits.

Oracle quickly moved to issue a patch after ShinyHunters began weaponizing the vulnerability in June. Concurrently, cybersecurity firm Mandiant released web application firewall (WAF) rules designed to protect organizations that could not immediately apply the security update.
While ShinyHunters initially told BleepingComputer in June that their primary objective was to breach the FBI’s internal PeopleSoft database—an attempt they claimed was initially unsuccessful—they later adapted. In subsequent weeks, the group utilized a well-known URL-encoding trick to bypass the WAF rules recommended by Mandiant.
On September 25, security experts at Mandiant and the Google Threat Intelligence Group (GTIG) published a joint report confirming that ShinyHunters had mass-exploited the PeopleSoft vulnerability. The campaign compromised dozens of systems across diverse sectors, including higher education, technology, healthcare, agriculture, transportation, and government agencies.
Further fallout from the campaign emerged when Reuters reported that the FBI had removed an Accenture contractor over their failure to patch the compromised FBI recruitment portal. The breach exposed sensitive personal data belonging to more than 5,000 FBI personnel, including individual unit assignments, professional specializations, and confidential medical and psychiatric records.
"Rey" Means King, as in Royal
According to two sources familiar with the ongoing international investigation into ShinyHunters, a digital aviation and navigation unit divested by Boeing was among the primary targets undergoing extortion when Rey was captured by Jordanian authorities. The investigation gained intense urgency due to the nature of the stolen data from the former Boeing division, which officials warned could introduce operational safety and security risks.
In a statement provided to KrebsOnSecurity, Boeing acknowledged the extortion attempt and confirmed that the incident involved data stolen from Jeppesen ForeFlight. Boeing sold the subsidiary in November 2025 to private equity firm Thoma Bravo for $10.55 billion.

"We are aware of claims by a threat actor regarding data allegedly associated with Boeing and our former subsidiary Jeppesen ForeFlight," a Boeing spokesperson stated. "Estamos actively reviewing the matter with the Jeppesen ForeFlight team."
A representative for Jeppesen ForeFlight added that internal operations remained unaffected. "Based on our investigation to date into this claim and proactive security posture, there was no impact to our operations or products."
Rey’s alleged connection to the extortion attempt carries additional weight due to evidence indicating his father works for Royal Jordanian Airlines, a carrier predominantly controlled by the Jordanian government that operates long-haul flights using Boeing aircraft. While Rey claimed on Telegram in early 2025 that his father was an airline pilot—a detail that could not be independently verified—password-stealing malware recovered from a shared family computer revealed login credentials belonging to his father used across multiple internal Royal Jordanian Airlines portals.
Royal Jordanian Airlines did not respond to requests for comment. Shortly after KrebsOnSecurity reached out to Rey’s father to apprise him of his son’s alleged illicit activities, Rey began systematically purging his social media footprint, including the Twitter/X handle used to taunt federal investigators and ransomware gangs.
Despite deleting his mainstream social media profiles, Rey’s GitHub-hosted cybersecurity blog remained online. In March 2026, the blog published a comprehensive investigative post doxing two Russian men identified as the core developers and hackers behind the Cl0p ransomware operation.
Murder-for-Hire Allegations in the Netherlands
Meanwhile, Dutch media outlets published explosive allegations concerning Pepijn van der Stap, whose narrative of personal rehabilitation and transition into legitimate cybersecurity work had previously received widespread media coverage. Daily newspaper RTL reported on September 29 that investigators suspect Van der Stap attempted to commission at least two murders abroad.

Van der Stap had recently completed the majority of a four-year prison sentence for data theft and extortion, crimes prosecutors stated netted between €1.5 million and €2.7 million. Prior to his September 15 arrest, Van der Stap interviewed with KrebsOnSecurity on September 9, presenting himself as the "offensive security lead" at Dutch cybersecurity firm Neo Security, where he claimed to test client networks for vulnerabilities.
Benjamin Korper, the owner of Neo Security, told Reuters that he hired an independent firm to investigate whether Van der Stap had compromised Neo Security or its clients. Investigators reportedly found no evidence of internal malicious activity. Korper confirmed that Dutch forensic teams visited his office on the night of Van der Stap’s arrest—a raid that reportedly involved the deployment of flash-bang grenades by specialized tactical units.
Before his initial arrest in 2023, Van der Stap worked as a software engineer at Amsterdam-based cybersecurity startup Hadrian while volunteering for the Dutch Institute for Vulnerability Disclosure (DIVD), even as he covertly hacked and extorted major global organizations. When questioned about how the public could trust a self-described reformed cybercriminal, Van der Stap maintained that his actions in cybersecurity remediation would have to speak for themselves.
Franchising and Burning a Brand
Cybercriminals operating under the ShinyHunters banner have been linked to dozens of major data breaches spanning billions of records since at least 2019. However, cybersecurity experts emphasize that the modern operators utilizing the name are distinct from the group’s original core members, most of whom are French citizens previously arrested or imprisoned for cybercrime.
Security analysts compare the modern evolution of ShinyHunters to a franchise model akin to the literary "Dread Pirate Roberts" character, where succession is driven by law enforcement arrests rather than death, allowing multiple individuals to adopt the moniker simultaneously. Investigators believe the FBI is currently focusing on a remaining network of freelance cybercriminals who feed stolen SaaS platform credentials to affiliates in exchange for a percentage of any ensuing ransom payments.
In the wake of Van der Stap’s arrest, a Telegram chat server reportedly operated by Rey became a hub of criticism from other cybercriminals. Participants mocked the teenager after he publicly backed down from threats made against the FBI and Cl0p, and after the ShinyHunters darknet portal abruptly went offline.

Commentators accused Rey of appropriating the dormant ShinyHunters brand after French authorities rounded up the original members, using the reputation of the group to orchestrate independent extortion schemes.
A newly emerged Telegram channel titled "The Battle" has spent weeks doxing and taunting Rey and other alleged associates, characterizing the teenager as an inexperienced newcomer attempting to capitalize on a notorious cybercrime brand.
"Rey (Saif Al-Din Khader) made a serious mistake when he started pretending to be a member of ShinyHunters," wrote the administrators of The Battle. "That group had already been dismantled, with many of its members either arrested or imprisoned, yet Rey still chose to use its name while carrying out his crimes."
In a prior interview with The Register, representatives for the modern iteration of ShinyHunters asserted that their decision to target the FBI was intended to counter the narrative presented in an agency flash notice published on May 15, 2026, which advised organizations against paying ransoms. The hackers admitted that while the FBI’s public advisory significantly damaged their ability to convince victims to pay, the attack served as a high-profile public relations maneuver designed to demonstrate their technical capabilities in the face of federal warnings.

Comments (0)