


According to a comprehensive technical report released today by the Google Threat Intelligence Group (GTIG), the tech giant has officially severed all business and operational ties with Videostrong Technology Co., a prominent TV box manufacturer located in China. GTIG, working alongside various industry security analysts, concluded that Videostrong was directly responsible for baking the malicious software straight into the device firmware. This malicious payload successfully enrolled more than 1.3 million consumer set-top boxes into a sprawling botnet officially dubbed "XCPE," a designation derived from one of the malware’s core system code components.
The mechanism behind the XCPE botnet was designed to quietly monetize household bandwidth without the knowledge or explicit consent of the device owners. Once active, the malware loaded affected devices with specialized software that dynamically made the user’s unique internet protocol address available for commercial resale by multiple "residential proxy" services. These commercial proxy operations allow external customers—ranging from legitimate businesses to malicious actors—to rent residential IP addresses to completely anonymize their web traffic, bypass geographical restrictions, or mask their true physical locations.
While residential proxies have legitimate commercial applications, industry investigations over the past several years have consistently revealed them to be a primary vehicle for launching malicious traffic. This includes sophisticated account takeover attempts, large-scale ad fraud schemes, and automated, unauthorized mass content scraping operations frequently used to feed data into artificial intelligence projects.
Videostrong monetized this covert backdoor by aggressively selling direct access to various criminal affiliates, subsequently loading those affiliates’ custom malware modules onto the already infected consumer hardware, the GTIG report detailed. To combat this illicit infrastructure, Google initiated targeted legal actions to seize and neutralize the various domains and command-and-control servers that Videostrong utilized to manage the botnet and push unauthorized updates.
"A device manufacturer intentionally infecting their users with malware is an unacceptable breach of trust, and represents a serious risk to those users," the GTIG report stated. "Without users’ knowledge or consent, infected devices were offered as a distribution mechanism for a wide array of criminal actors."

While standard consumer television boxes constituted the vast majority of the botnet’s footprint, researchers discovered that the exact same XCPE malware strain was embedded in various other Android-based IoT products. These included specialized telehealth devices, commercial and residential karaoke machines, and digital displays used for advertising, highlighting a systemic supply chain vulnerability across multiple product categories.
Google maintains strict requirements that all Android device manufacturers must successfully pass comprehensive compatibility and security evaluations to guarantee their hardware does not compromise user safety. However, investigators found that Videostrong managed to circumvent these safeguards by engineering the malware to execute and install itself immediately after a consumer booted up a brand-new device for the very first time. Google confirmed that it has since implemented security patches and protocol adjustments to address and eliminate that specific vulnerability.
The GTIG threat report explicitly called out several notable residential proxy providers whose software development kits were routinely downloaded, installed, and leveraged by devices trapped within the XCPE botnet. Among those named is AppSalt, also widely known as Honeygain, which is owned by Oxylabs, a prominent data intelligence company based in Vilnius, Lithuania. Oxylabs underwent a major corporate relaunch under a new brand called Source, following a substantial $130 million funding injection from private equity firm Warburg Pincus that reportedly valued the enterprise at approximately $3.6 billion. Representatives for Oxylabs did not respond to multiple requests for comment regarding their connection to the botnet infrastructure.
Another major residential proxy provider linked directly to the unfolding botnet crisis is NetNut, a sprawling proxy operation previously operated by Alarum Technologies, a publicly traded Israeli firm. The federal law enforcement apparatus, including the FBI, partnered with private cybersecurity researchers to seize hundreds of internet domains associated with NetNut. Authorities stated at the time that the company was responsible for orchestrating a completely separate, massive botnet named Popa, which similarly enslaved consumer streaming boxes to act as unwitting residential proxies. Additional proxy services explicitly named in the Google Threat Intelligence Group report include EarnFM, Traffmonetizer, Jaguar, LINKFOG, BMW/IPWeb, and GaGaNode.
Google’s public announcement of the takedown gave significant credit to a number of crucial industry partners, most notably Synthient, a specialized security startup that continuously tracks and analyzes proxy infrastructure. Earlier in the year, Synthient published groundbreaking research documenting the explosive, rapid spread of the Kimwolf botnet. At the time of its discovery, Kimwolf was actively bombarding enterprise networks worldwide with record-breaking distributed denial-of-service attacks. Synthient’s investigation detailed precisely how Kimwolf infected millions of Android set-top boxes almost overnight by exploiting a widespread vulnerability inherent in residential proxy services, subsequently using those infected hubs to compromise other vulnerable Android devices residing on the local home networks of unsuspecting consumers.
The publication of Synthient’s research prompted dozens of residential proxy providers to hurriedly patch their vulnerable networks. This defensive action successfully fractured the monolithic Kimwolf botnet into smaller, manageable fragments, significantly blunting its incessant and disruptive DDoS capabilities and making mitigation far simpler for network operators. The research also drew the intense focus of the Motion Picture Association, the major Hollywood studio trade organization, which partnered directly with Synthient to purchase, disassemble, and analyze numerous popular Android TV set-top boxes, including several heavily infected by Kimwolf and related IoT botnets.

In a companion technical report published concurrently with Google’s announcement, Synthient examined a popular, pre-infected TV streaming device sold under the brand name MECOOL by Skyworth Technology, a publicly traded technology company based in China. Synthient concluded that MECOOL hardware also bundled the malicious payloads originating from Videostrong Technology Co., while similarly pre-installing AppSalt, Honeygain, and other related proxy software components.
Synthient founder Ben Brundage noted in discussions regarding the research that Videostrong’s persistent malware network also actively distributed software components for another proxy service known as Grass. Previous industry investigations by independent security researchers at Censys uncovered similar unauthorized bundling of Grass’s residential proxy software inside popular Superbox TV streaming devices, though representatives for Grass consistently denied any direct corporate affiliation with the TV box manufacturers.
Superbox and similar gray-market Android TV boxes traditionally acquire vast customer bases by partnering heavily with social media influencers on platforms like TikTok. These influencers frequently promote the hardware by highlighting its ability to deliver hundreds of pay-per-view and premium television streaming channels for a single, low, up-front fee, effectively masking the underlying infrastructure of pirated content and malware.
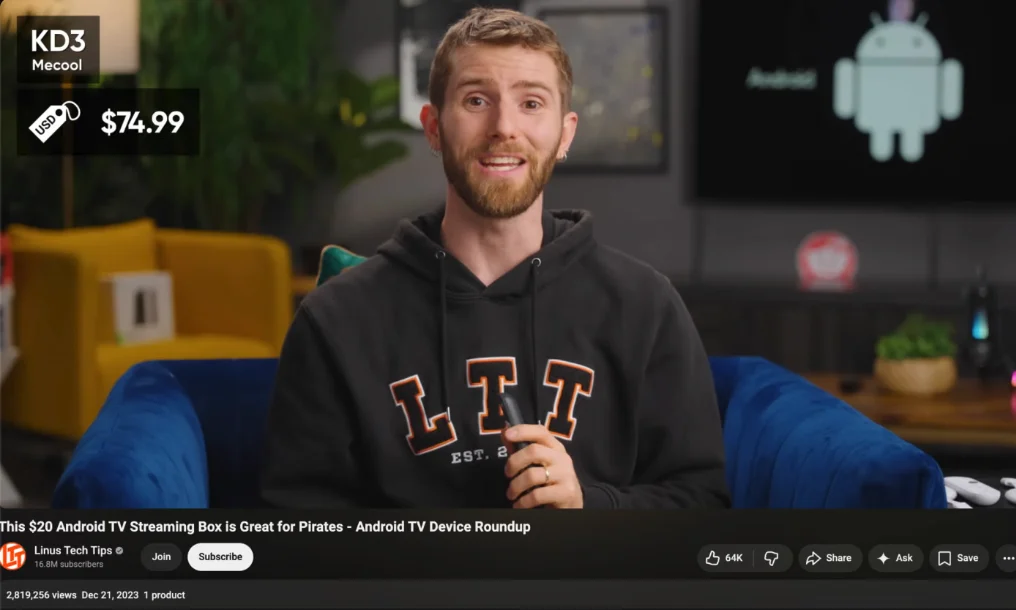
Similarly, Synthient’s research highlighted that MECOOL set-top boxes experienced an explosive surge in mainstream popularity after the hardware was featured prominently in content produced by the massive YouTube channel Linus Tech Tips, which boasts an audience of nearly 17 million subscribers. Representatives for Linus Tech Tips shared a statement with Synthient confirming that the channel has since updated the original video to explicitly categorize the product as a consumer scam and permanently removed all associated commercial affiliate links.
While the primary takedown directly neutralized 1.3 million active devices running the XCPE core, the GTIG report emphasizes that this figure represents only a fraction of the total threat landscape. Because Videostrong’s various proxy and advertising fraud affiliates maintained diversified, independent distribution channels for their individual modules extending well beyond the XCPE framework, the true scale of infected hardware remains significantly higher.
Synthient founder Ben Brundage echoed this assessment, describing the verified 1.3 million device figure as highly conservative. He noted that the total scope of affected consumer devices is likely far greater, characterizing the multi-agency operation as the largest coordinated strike against backdoored consumer TV streaming boxes documented to date.

Comments (0)