


Security experts have revealed that several staffers inside the White House are utilizing computers and mobile devices equipped with residential proxy services, inadvertently rendering their secure internet addresses available for rent to outside parties.
According to findings released by cybersecurity firms, the alarming oversight leaves critical digital infrastructure open to anonymous external traffic. Most concerningly, one of the primary proxy services linked to the network activity is a Russian company whose founder has a documented history tied to cyberattacks targeting U.S. state election systems.
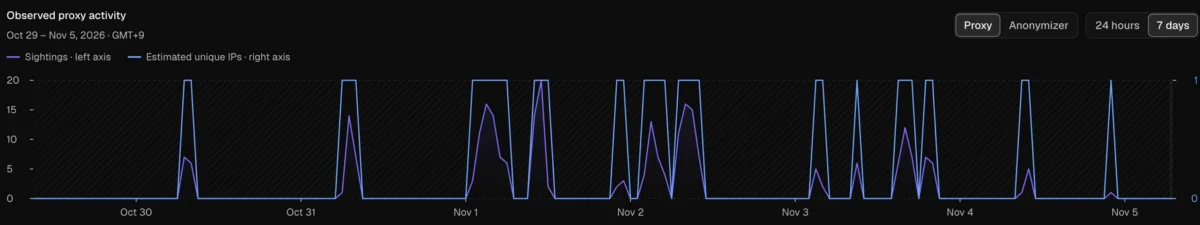
The security firm Layer3 Intel announced that it detected multiple residential proxy nodes beaconing outward from the dedicated internet address network reserved for the Executive Office of the President, designated as AS2650. Investigators noted that the proxy activity demonstrated a relatively persistent pattern between October 5 and November 3. A comprehensive review of the active proxies available through AS2650 revealed that they successfully exited from the heavily guarded White House network 236 times during that specific timeframe.
Simultaneously, proxy tracking and intelligence company Synthient reported via social media that the suspicious activity originating from AS2650 was directly tied to multiple Windows 11 installations running a service called Infatica. Infatica is a commercial proxy program frequently bundled and integrated into ostensibly "free" mobile and desktop applications downloaded by everyday users.
The background of Infatica’s leadership adds a severe geopolitical and counterintelligence dimension to the discovery. The company’s founder is Vladimir Fomenko, a Russian national whose previous web hosting firm, King Servers, served as the infrastructure ground zero for cyberattacks against election databases in Arizona and Illinois in 2016. At that time, King Servers hosted six of the eight specific internet addresses utilized by Russian state security services to infiltrate and compromise state election systems.
The mechanics of residential proxy services generally involve users unknowingly trading away the bandwidth of their home or workplace internet connections in exchange for free software features or application perks. There are dozens of residential proxy providers operating globally with varying degrees of legitimacy, with many headquartered or heavily tied to jurisdictions in China and Russia.
At their core, these services simplify the process for paying customers to rent someone else’s legitimate internet address. This practice allows malicious actors, corporate scrapers, or privacy-seeking individuals to completely anonymize their web traffic or spoof their true geographic location. From the perspective of any target website, the incoming traffic appears to originate directly from the rented IP address—such as one belonging to the White House—rather than from the actual proxy service customer who is directing the activity.
Layer3 Intel reported that the proxy exit nodes operating out of the White House network originated from six distinct internet addresses across 26 of the 30 days monitored by the firm. Researchers observed that the vast majority of this unauthorized activity took place during evening hours, specifically clustering between 5 p.m. and midnight local time.
Incredibly, further analysis showed that Infatica was not even the sole proxy service reselling access to White House internet addresses. Layer3 Intel discovered that an astonishing 28 separate residential proxy services were capable of routing traffic and exiting through this vital government network.
Describing the ease with which outside parties could tap into the network, the Layer3 Intel research team explained that the infrastructure functions as public access. According to the firm, anybody can obtain access simply by signing up for a public residential proxy service, paying a few dollars, and routing their digital requests through it. The researchers emphasized that they did not selectively target the White House network or attempt to force their probes to exit from it; rather, they stumbled upon the vulnerability purely by chance while requesting global rotating access through these commercial services.
The White House did not immediately respond to requests for comment regarding the security findings.
Security researchers note that residential proxy services have increasingly become a major vector for unwanted and inherently malicious internet traffic. Over the past year, these networks have been heavily implicated in automated account takeovers, cybercrime operations, large-scale advertising fraud, and the aggressive harvesting of web content for artificial intelligence training projects.
Beyond mere nuisance traffic, these services introduce severe underlying security risks to any environment where they are deployed. In late 2025, security analysts discovered that cybercriminals were heavily exploiting a widespread structural vulnerability inherent to many proxy networks. This flaw allowed bad actors to systematically probe each proxy endpoint’s local network, hunting for vulnerable systems to infect with malware.
By January 2026, dozens of proxy services were forced to scramble and patch their networks after Synthient Founder Ben Brundage publicly demonstrated how cybercriminals were actively abusing these vulnerabilities to seize absolute control over devices residing inside the local networks of unsuspecting users.
Brundage noted that the underground economy surrounding these services makes high-level network intrusion remarkably cheap and accessible. He pointed out that some commercial resellers market bandwidth for as low as 60 cents per gigabyte, meaning that for less than a dollar, an adversary can purchase a bridge into some of the most confidential and trusted networks in the world. Furthermore, the broader reseller ecosystem exacerbates the problem by allowing criminal buyers to bypass standard Know Your Customer, or KYC, verification processes entirely.
All too frequently, these dangerous proxy connections find their way onto corporate and government networks because employees inadvertently bring infected or improperly configured personal devices into the workplace. Software and mobile app developers routinely embed Software Development Kits, commonly known as SDKs, provided by residential proxy networks to monetize their products, offering developers a small financial kickback for every installation completed by an end user.
Despite the obvious dangers, residential proxies are remarkably pervasive across high-security environments. During a security webinar held in January 2026, proxy tracking service Spur revealed that it had detected residential proxies operating within nearly 300 government-owned and operated networks. The same tracking data identified proxies inside 318 utility companies, 166 healthcare organizations and hospitals, and 141 firms operating within the banking and finance sectors. Additionally, a security advisory published earlier this year by Infoblox reported that a staggering 65 percent of its enterprise customer base had queried one or more residential proxy-related domains from within their corporate perimeters.

Comments (0)