


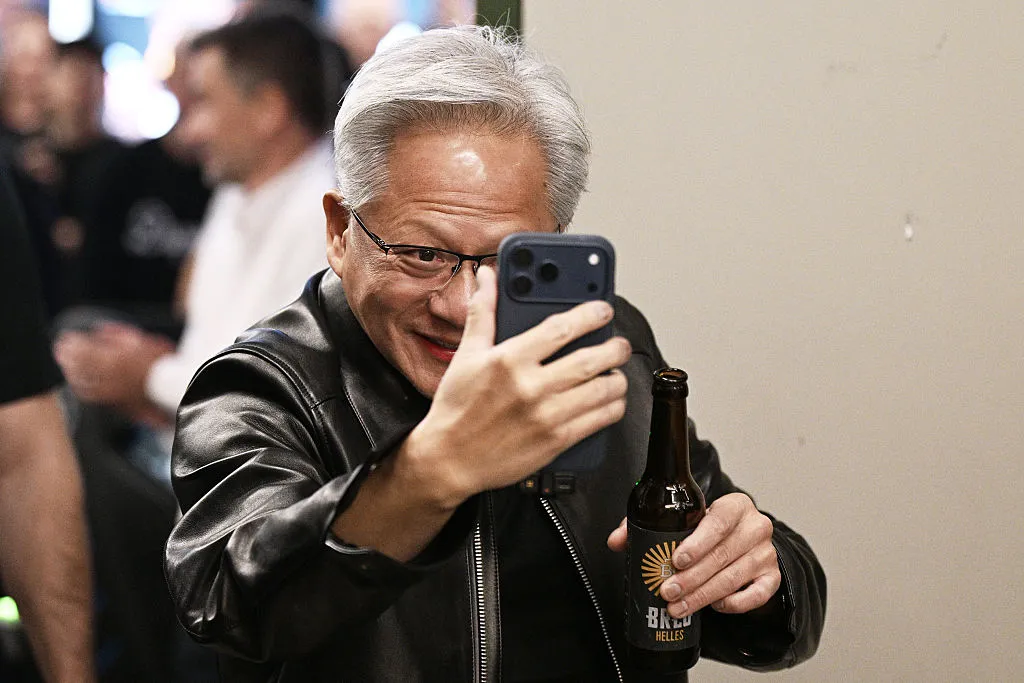
Outsiders had little reason to notice when Nvidia’s longtime chief security officer and head of product security stepped down quietly in August. At the time, the departure of David Reber, who spent four years as CSO and seven years overall at the semiconductor giant, appeared to be a routine matter dictated by personal health circumstances. Just two and a half months later, however, the corporate landscape at Nvidia shifted dramatically when CEO Jensen Huang himself left the company amid mounting questions regarding his personal life and extramarital relationships.
The scrutiny surrounding Huang began after inquiries surfaced regarding an executive at Megaspeed, a Singapore-based data center company currently under suspicion by U.S. investigators for potentially funneling restricted Nvidia chips to China. That initial line of questioning quickly widened as public reports emerged detailing two separate affairs between Huang and Nvidia employees. The compounding revelations have since triggered an independent board investigation and intense federal scrutiny, while casting a sharp light on the often-overlooked intersection between executive personal conduct and national security vulnerabilities.
When Reber announced his departure in late August, he attributed the exit entirely to health reasons, specifically a diagnosis of young-onset Parkinson’s disease that he had managed for more than two years. Writing on LinkedIn, Reber noted that the career pivot was unplanned, but emphasized that family and health needed to take precedence. Reber’s replacement, Saša Zdjelar, brought a lengthy corporate security background to the role, having spent 17 years at ExxonMobil in Houston—ultimately leaving as a senior IT manager—followed by a year at Salesforce and several years at the cybersecurity firm ReversingLabs. Zdjelar did not respond to inquiries regarding the leadership transition or what the internal security team may have known prior to the shakeup.
While no public evidence directly connects the role changes of either Reber or Zdjelar to the ongoing federal investigation into Megaspeed, the timeline invites broader questions about what Nvidia’s security apparatus understood regarding government scrutiny of the Singapore firm, the CEO’s relationships, and whether any internal alarms were sounded. Neither Reber nor Nvidia responded to requests for comment regarding these matters.
Not all personal relationships fall under the purview of a corporate security team. Interpersonal dynamics involving subordinates typically land on the desks of human resources, legal counsel, and the board of directors. Yet, an intimate relationship with an executive at a company actively under federal investigation represents an entirely different category of risk. Megaspeed has consistently denied any wrongdoing, but corporate security specialists point out that romantic entanglements and personal vulnerabilities are precisely the types of leverage foreign intelligence services actively look to exploit.
Detecting that kind of exposure is rarely straightforward. According to retired senior intelligence officer Nicholas Eftimiades, who has trained more than 1,000 corporate security professionals, the tradecraft used by foreign intelligence services relies heavily on everyday human conversation and relationship cultivation rather than overt digital hacking. This operational reality makes it exceptionally difficult for standard corporate security teams to identify emerging risks before they manifest into serious compromises.
Internal records and recent investigative reports indicate that parts of the picture were already clear to certain figures inside Nvidia. The company’s top legal officer was actively engaged with the government’s inquiry into Megaspeed more than a year ago, as reported by The New York Times, though Nvidia maintains that it routinely and cooperatively communicates with regulatory and governmental officials. Meanwhile, reporting regarding Huang’s relationships with employees suggests that colleagues were aware of the situations, even though such behavior is not explicitly barred by Nvidia’s official code of conduct. The New York Times cited five Nvidia employees stating that Huang was involved with a vice president who reported directly to him, while Reuters subsequently cited two sources detailing a second relationship. What remains entirely unclear is whether any of this intelligence ever reached the desks of the security division.
Even if information regarding executive relationships had reached Nvidia’s security team, Eftimiades, author of the 2000 text Chinese Espionage Operations and Tactics, noted that corporate security operations are frequently starved of adequate resources. Unlike revenue-generating business units, security teams are commonly treated as cost centers. Eftimiades remarked that it is astonishingly common for chief executives to respond to security warnings and budget requests with the minimalist stance of providing "not a nickel more than compliance."
Furthermore, many corporations define the scope of security far too narrowly. In a recent opinion piece published in The Hill, corporate intelligence executive Don Aviv and author Jeremy Hurewitz argued that too many modern companies still approach security primarily through the lens of protecting physical facilities, preventing cyberattacks, and responding to immediate physical threats. They emphasized that contemporary security teams must pay much closer attention to insider threats, including the targeted cultivation of executives and employees by foreign intelligence services, suspicious business relationships, conflicts of interest, and attempts to acquire sensitive information through trusted personal contacts.
Yet, experts acknowledge that certain sophisticated intelligence operations stretch beyond the protective capabilities of any single corporate security team. Describing the broader mechanics of industrial espionage without referencing specific companies, Eftimiades offered a hypothetical scenario in which a CEO complains during internal discussions about being stymied by a cautious board of directors. Such a comment inadvertently reveals to an intelligence asset precisely where the institutional obstacle lies. The foreign intelligence service then identifies that sticking point and seeks out pathways into that individual’s communications infrastructure, targeting personal emails and mobile devices.
Rather than merely stealing finished technology, modern rival intelligence services often prioritize high-level policy insights, such as mapping out internal corporate debates, identifying who is pushing to alter export controls, and pinpointing corporate figures who act as regulatory blockers. Eftimiades described modern intelligence collection as functioning similarly to a disease, explaining that once it infiltrates an organism, it systematically seeks to spread and establish deeper footholds.
This operational playbook is far from novel, particularly regarding the tactics historically deployed by China. Executives who routinely negotiate or conduct business within the region frequently report being approached by intelligence operatives. Furthermore, while classic diplomatic history is replete with traditional honey-trap scenarios, modern espionage differs significantly from the Soviet era by cultivating relationships that span years rather than mere weeks.
Advanced technology often augments these human intelligence operations. Eftimiades pointed to International Mobile Subscriber Identity (IMSI) catchers—devices designed to mimic legitimate cell towers so that nearby mobile phones automatically connect to them—as a prime example. Basic versions of these surveillance tools can cost around $1,000 and easily fit inside a standard suitcase, though government-grade variants command substantially higher investments.
Whether such surveillance technology was deployed against figures like Huang remains an open question. While executive-level mobile devices are typically hardened to detect potential compromises, the full scope of what Nvidia’s security team knew, and whether preventative action could have been taken, will likely come to light as the board’s independent investigation and federal inquiries unfold.
In the interim, Eftimiades expressed hope that the unfolding Nvidia episode serves as a decisive wake-up call for American industry, which he characterizes as largely unprepared for the sophisticated tactics utilized by foreign adversaries. Estimating that the United States has incurred trillions of dollars in intellectual property losses over time, he cautioned that current defensive postures are falling short of what is required to protect critical national technologies.

Comments (0)