


The chief technology officer and co-founder of ransomwarehelp.com, a Florida-based business that spent six years marketing itself as a premier digital rescue service utilizing “advanced cryptographic tools” to restore data locked during cyberattacks, has been formally charged with wire fraud. According to federal court documents, an elaborate FBI sting operation exposed that the firm possessed no proprietary decryption technology whatsoever. Instead, the company was simply paying threat actors behind the scenes for decryption keys, concealing their actions, and charging victim companies exorbitant markups for complex technical labor that was never actually performed.
The website for RansomwareHelp aggressively courted panicked business owners with bold slogans such as “Do not pay the ransom!” It assured prospective clients that its proprietary cryptographic mechanisms could successfully recover 100 percent of locked data, servers, and systems back to their original formats, thereby eliminating any necessity to cave into the demands of digital extortionists.
“Our cryptography experts use proprietary tools and algorithms to achieve 100% data recovery, all backed by a success rate of over 99%,” the website proclaimed, weaving an intricate narrative that the enterprise boasted more than 28 years of collective experience alongside a workforce of 80 specialists spanning cryptography, cybersecurity, forensic analysis, and reverse engineering. “We never promote, intermediate or pay ransom to threat actors on behalf of our clients.”
However, an indictment unsealed this week in Rhode Island reveals a starkly different reality. The documents target the company’s co-founder, 52-year-old Juan Ricardo Palacio Escobar, who divides his time between Miami, Florida, and Medellin, Colombia. Federal prosecutors state that Palacio routinely engaged with criminal ransomware gangs, secured decryption keys for victim companies under the table, and then billed those exact victims massive financial premiums vastly exceeding his covert acquisition costs. News of the indictment initially surfaced via reporting by 404 Media, though that initial coverage omitted the name of the defendant’s corporate entity.
The federal indictment outlines how the FBI initiated a carefully coordinated sting operation in which undercover agents played a dual role: acting simultaneously as a compromised business and posing as a fictitious ransomware syndicate. Investigators operating under the guise of an attacked firm reached out to RansomwareHelp, providing them with a simulated ransomware note while explicitly expressing their aversion to paying any extortion fee. In response, RansomwareHelp sent back boilerplate messaging reaffirming its strict corporate policy against negotiating with or making payments to threat actors.
Shortly after this initial contact, government documents state that Palacio reached out directly to the fictitious cybercriminal group orchestrated by the FBI, aggressively bargaining for the absolute lowest possible price for a decryptor. Federal investigators, maintaining their undercover persona, countered with an initial price tag of 0.2 bitcoin, which equated to roughly $13,000 at the time. Less than 48 hours later, Palacio allegedly contacted the agents posing as the victimized company, falsely reporting that a diagnostic assessment had been successfully completed and declaring that the total cost to decrypt the files would run $13,260.

The following day, according to the government’s timeline, Palacio turned back around and messaged the FBI’s fake ransomware cell, petitioning them to slash the extortion demand down to $4,000 in exchange for the decryption tool. The indictment notes that an agreed-upon settlement price of roughly $6,000 in bitcoin was eventually struck with the undercover agents, while Palacio simultaneously charged the fake victimized enterprise a grand total of $16,010, which incorporated an upfront $2,750 diagnostic fee stacked on top of the inflated $13,260 processing charge.
Industry experts have long suspected foul play among unscrupulous remediation vendors. Paul Ihme, co-founder of the security firm Soteria, recalled in an interview with KrebsOnSecurity that he was contacted back in 2024 by a small accounting firm desperately trying to recover from a devastating Lockbit ransomware infection that had completely paralyzed its corporate network and client files.
According to Ihme, RansomwareHelp provided that vulnerable accounting firm with a formal project proposal carrying a staggering recovery price tag of $438,880. The proposal claimed this immense figure covered the “professional configuration of forensic servers,” “expert engineering hours of programming to configure decryption algorithms,” and multiple intensive processing cycles dedicated entirely to unlocking the data.
The formal proposal further asserted that the complex data recovery procedure necessitated reverse engineering the underlying ransomware encryption utilizing “510 preconfigured forensic servers of the maximum quantitative capacity located in different parts of the world.”
“Our programmers will inject randomly the encryption codes extracted during the forensic and cryptographic analysis using brute force processes,” the company’s pitch claimed.
Ihme noted that RansomwareHelp heavily pressured the accounting firm to grant them unrestricted, unmonitored remote access into their corporate network to perform their diagnostic evaluations, instructing them to install AnyDesk remote desktop software. Ihme believes this insistence on remote access served a dual purpose, allowing the scammers to surreptitiously erase all digital copies of the actual ransom notes left behind across the victim’s network by the authentic threat actors.
Standard ransomware attacks typically scatter numerous plain text files across infected machines. These notes introduce the attacking syndicate, detail their monetary demands, and provide a direct communication channel—frequently an email address or a darknet live chat portal.

However, when Ihme’s team reviewed the accounting firm’s network infrastructure during the incident response, they managed to unearth only a single surviving copy of the ransom note buried deep inside a backup snapshot on an infected computer. Upon plugging the provided user identification credentials into the Lockbit chat server, they uncovered an unsettling discovery: an unknown third party had already been actively negotiating with the Lockbit extortionists for several days.
“The charitable view would be to say that they were using AnyDesk so they could grab the stuff they needed without having to walk the client through downloading and uploading a bunch of stuff,” Ihme observed. “A legitimate firm would say, ‘Hey, send us a copy of the ransom note,’ which will have a link or URL to go to and chat with the threat actors. What they were doing is using that access to delete ransomware notes off the systems. The only reason they would do that is to prevent the victim from jumping into that chat itself.”
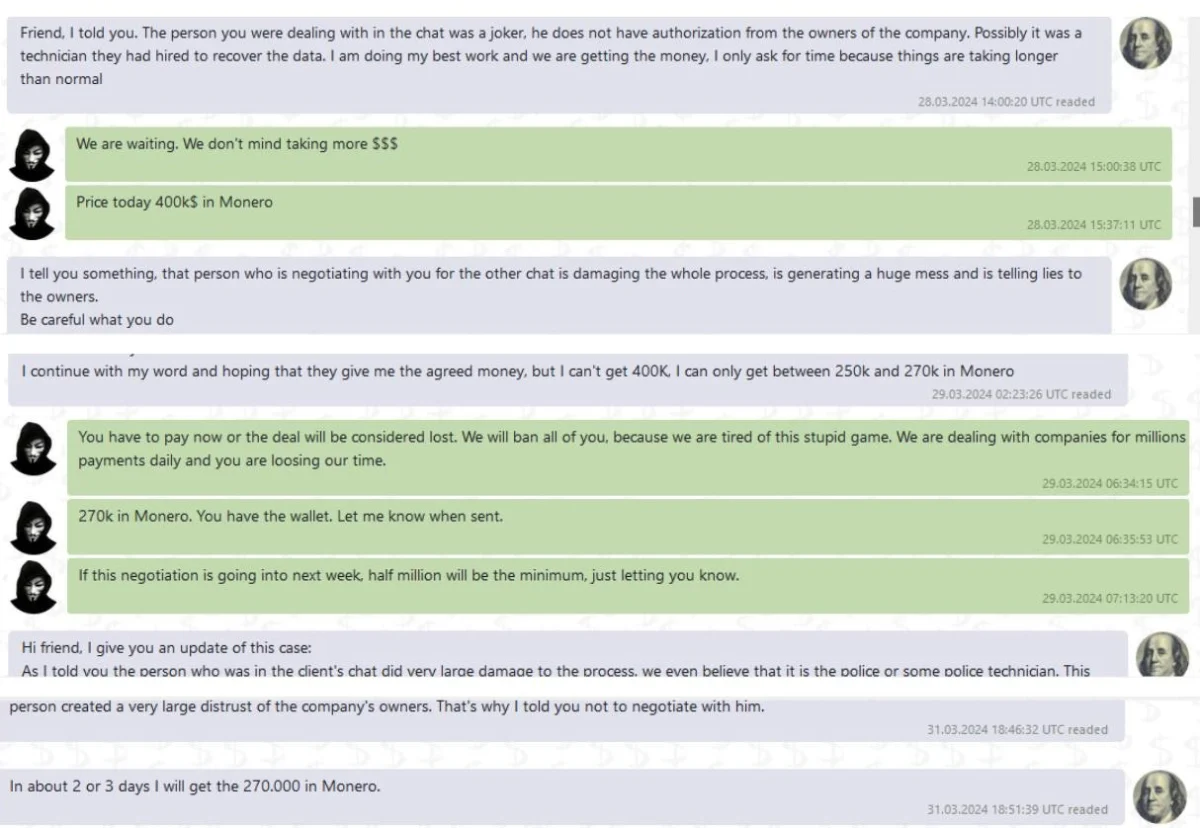
Transcripts of the chat logs demonstrate that RansomwareHelp repeatedly begged the Lockbit gang to keep their corporate involvement secret from the actual victims. Yet, the Lockbit operators quickly grew frustrated with the sluggish pace and back-and-forth maneuvering, warning that the victims had delayed too long and that the baseline ransom demand would automatically escalate by $100,000 for every single day talks dragged on.
Ultimately, the accounting firm heeded Ihme’s professional advice, severed ties with RansomwareHelp, and retained a reputable incident response firm that successfully negotiated a direct payment with Lockbit at a fraction of the quoted expense.
“The victim told us, ‘If we don’t get this data back, our business is over,’” Ihme remembered. “They ended up paying half of what RansomwareHelp was going to charge them.”
Even as independent negotiators stepped in on the victim’s behalf, chat records show that RansomwareHelp continued to badger Lockbit representatives in an apparent attempt to maintain control over the illicit transaction.
“I tell you something, that person who is negotiating with you for the other chat is damaging the whole process,” RansomwareHelp wrote to Lockbit in the recovered logs. “Please do not change the price. I am doing my best to achieve it.”

Ihme emphasized that companies like RansomwareHelp deliberately preyed upon small-to-medium-sized enterprises lacking internal technical oversight, pointing out that many of the high-sounding claims featured on the firm’s website and proposals were technically nonsensical. For instance, the proposal handed to the accounting firm claimed an ability to crack six different categories of encryption, yet proceeded to list irrelevant password hashing mechanisms such as SHA-256.
“If it were really true these guys could decrypt any ransomware out there, this guy would be a billionaire,” Ihme said. “They were going after people who don’t have any technical knowledge, are desperate, and don’t have anyone advising them about how any of this stuff works.”
The federal case against Palacio represents only the latest in an expanding wave of criminal prosecutions launched by the U.S. Department of Justice targeting dubious security intermediaries accused of colluding with cybercriminals to defraud vulnerable clients. In early October, federal authorities arrested 54-year-old Edward Dubrovsky, an executive at Canadian cybersecurity firm Cybersteward, who currently faces charges of cyber extortion and conspiracy.
Around that same period, the Department of Justice announced criminal indictments against MonsterCloud CEO Zohar Pinhasi, 50, hitting him with wire fraud and conspiracy charges. Prosecutors allege that Pinhasi similarly billed customers substantial sums to remediate ransomware attacks while covertly paying off hackers behind his clients’ backs, funneling roughly $8 million to ransomware syndicates while extracting $19 million from unsuspecting victims.
Earlier in the year, 41-year-old ransomware negotiator Angelo Martino of Land O’Lakes, Florida, was sentenced to 70 months in federal prison. Martino was convicted of conspiring with the Blackcat/ALPHV ransomware collective to extort multiple American businesses by secretly leaking confidential client negotiation strategies to the hackers, thereby empowering the cybercriminals to maximize their extortion payouts.

Comments (0)