


As the Ethereum ecosystem continues to scale and secure increasingly vast amounts of economic activity, the Ethereum Foundation’s Trillion Dollar Security initiative has flagged blind signing and transaction uncertainty as critical user experience and safety risks. To address these vulnerabilities, researchers are exploring native transaction assertions as a foundational mechanism to enforce the final outcomes of transactions, working alongside broader initiatives like Clear Signing.
This development focuses on why a cryptographically valid signature does not always guarantee the intended transaction result, how native transaction assertions could protect users beyond the limits of current defenses, and the underlying design choices required to implement such changes, with EIP-7906 standing out as a prominent approach.
Two Ways a Signed Transaction Can Go Wrong
The core challenge stems from the fundamental architecture of the Ethereum Virtual Machine (EVM). Ethereum executes transactions precisely as they are authorized, operating without an inherent understanding of whether the resulting state matches the user’s true economic intentions. While a signature serves as a binding commitment to a specific request, the ultimate outcome of that execution depends entirely on the code and network state encountered when the transaction is processed on-chain. Over the history of the network, users have suffered significant financial losses either because they authorized actions that differed drastically from what they believed they were approving, or because the request they intended to make still produced an unfavorable, divergent result.
The first category of failure is an intent mismatch, a phenomenon vividly illustrated by historical security incidents such as the Bybit compromise and the BadgerDAO attack. In both of these events, compromised frontends supplied signing requests that deviated from what users thought they were validating. During the Bybit incident, signers inadvertently authorized the replacement of a Safe multi-sig implementation contract, while BadgerDAO users unknowingly granted malicious actors sweeping permissions to spend their underlying tokens.
The second major category involves an outcome mismatch. In these scenarios, the signer successfully approves the exact request presented to them, but existing constraints or the prevailing state of the blockchain allow an outcome that directly conflicts with their economic objectives or standing safety policies. A prominent example of this occurred during the Aave and CoW collateral swap event. A user attempted to swap approximately $50.4 million worth of aEthUSDT for aEthAAVE. Because the liquidity for AAVE was far too thin to support a trade of that magnitude, and because CoW’s gas ceiling rejected more complex quotes during the verification phase, only a single verified quote of roughly 329 aEthAAVE remained.
Although the interface displayed a drastic 99.9 percent price impact warning and explicitly required confirmation that the entire value could be lost, the user signed the transaction anyway and received tokens valued at roughly $36,000.
Across all three of these incidents, a common architectural gap was missing: a trusted rule governing the resulting state that was defined independently of the transaction builder and enforced directly at the execution layer. In the Bybit scenario, a protective rule would have mandated that the approved Safe implementation remain completely unchanged. For a BadgerDAO user, a policy would have permitted new token approvals exclusively for verified, published Badger contracts. For the Aave user, an effective rule would have established a mandatory minimum acceptable output calculated independently of the quotes provided by the frontend interface. Presently, however, Ethereum lacks a generalized mechanism for on-chain code to inspect the comprehensive set of net state changes and emitted events produced by a single transaction.
What a Signature Does Not Control
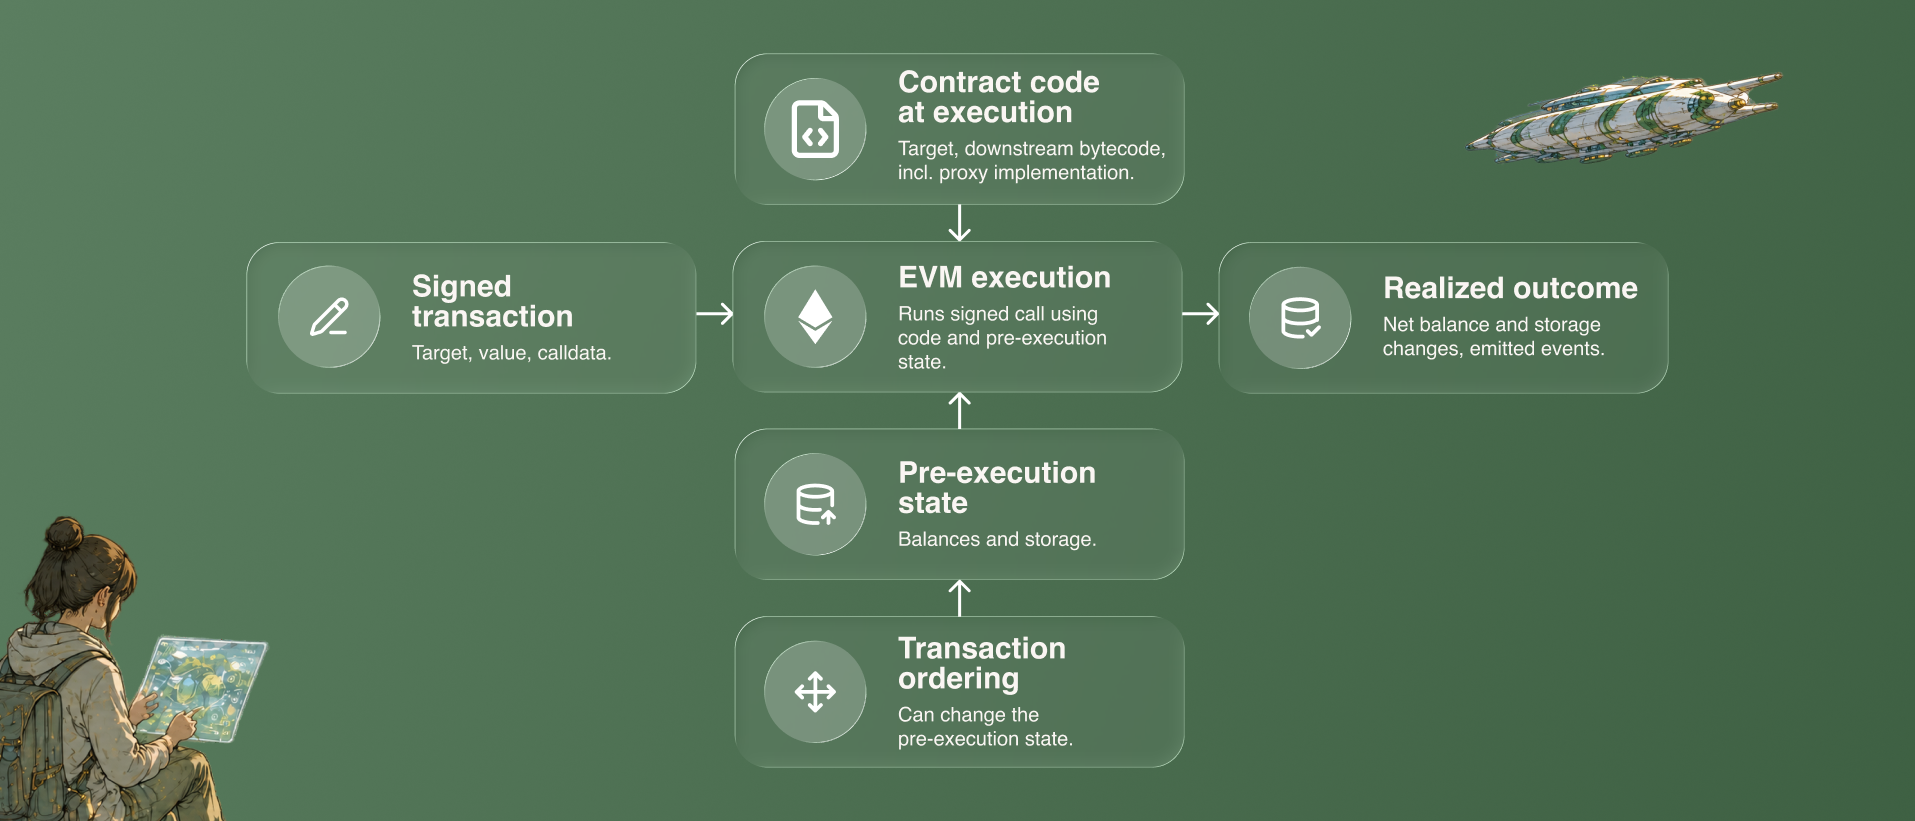
When a user signs a transaction, their signature cryptographically commits to a specific requested action, including the target contract, value, and calldata. However, the EVM executes this call against the exact contract code and blockchain state present at the moment the transaction is included in a block, which may have shifted significantly since the moment of signing. Consequently, the resulting net balance changes, storage updates, and emitted events can diverge widely from initial expectations.
The target contract involved—or another contract it calls—may utilize a proxy pattern whose implementation changes prior to execution, meaning the active code running on-chain differs from what the user inspected in their wallet interface. Furthermore, transaction ordering and adversarial manipulation can dramatically alter the state encountered by a call. For instance, a sandwich attack can artificially shift a decentralized exchange liquidity pool’s price immediately before a swap executes, all without altering the contents of the user’s signed transaction.
Where Today’s Defenses Stop
The Ethereum ecosystem already relies on several defensive layers to mitigate these risks. One key approach is Clear Signing, which aims to translate complex calldata into human-readable descriptions of the requested action. However, this defense depends entirely on accurate transaction decoding and on the signer’s ability to recognize discrepancies between the decoded action and their true intent.
Another prevalent defense is transaction simulation, which attempts to predict the effects of a transaction using a snapshot of the chain state. Despite its utility, the chain state can change before inclusion, and a compromised environment can result in a signed transaction that differs entirely from the one simulated. In the case of Radiant Capital, both the wallet interface and the underlying simulation accurately displayed the intended transaction, while malware operating locally on the signers’ machines substituted a malicious payload at the exact moment of signing.
Contract checks and built-in wallet guards also enforce specific rules during EVM execution. For example, Uniswap automatically reverts a swap if the final output falls below a pre-set amountOutMinimum. Similarly, Safe’s checkAfterExecution hook enables a guard to inspect an account’s state after execution and revert transactions that violate predefined governance rules.
Nevertheless, these existing mechanisms require developers to choose which specific state variables to check in advance. To read another contract’s storage, they must rely strictly on the public functions exposed by that contract. While checking a token’s balance via standard functions is straightforward, a proxy contract is not obligated to expose its implementation address through an accessible view function. Without such an exposed interface, a standard guard cannot read the underlying implementation storage slot directly. Crucially, these checks cannot inspect a transaction’s comprehensive set of net state changes, meaning unintended side effects can easily bypass oversight.
How Native Transaction Assertions Work
Native transaction assertions would empower on-chain code to inspect the complete set of net state changes after all actions within a transaction have been executed. Utilizing read-only logic, an assertion compares starting values and final values against a predefined rule. If the execution violates this rule, the entire transaction reverts.
The rule itself is bundled directly into the transaction and signed alongside its primary actions. It can encompass net modifications to native token balances, storage slots, newly deployed contracts, and emitted events. This flexibility allows users to mandate a minimum received amount, cap spending limits, block unauthorized token approvals, preserve an account’s control logic, or restrict execution to an explicitly specified set of changes.
The origin of this rule is just as critical as the verification logic itself. If a compromised frontend were permitted to write the assertion, it could simply craft a rule that authorizes the attack. Therefore, a secure rule must originate from independently verified user intent, a standing account policy, or protocol-level logic that cannot be manipulated by vulnerable components.
Three Design Choices
Designing native transaction assertions requires navigating several fundamental architectural decisions regarding how the EVM exposes information, how assertion code accesses that data, and where specific opcodes are permitted to execute. Developers must determine whether the exposed information should include state changes, events, or both. Access options range from enumerating entries and looking up specific values to copying the entire set of changes directly into EVM memory. Additionally, architects must decide whether the new opcodes should be restricted to specialized transaction types and execution phases or made universally available across the EVM.
EIP-7906 as a Possible Solution
A leading proposal addressing these challenges is EIP-7906, which builds directly upon the frame transactions introduced in EIP-8141. A frame transaction structures execution as an ordered sequence of validation and action steps. EIP-7906 introduces a specialized, read-only POST_TX frame positioned at the very end of the transaction lifecycle specifically to evaluate the final outcome. While EIP-8141 has been scheduled for the Hegot upgrade, EIP-7906 has advanced to a "Considered for Inclusion" status without yet being formally confirmed for that specific network upgrade.
The architecture of EIP-7906 exposes both net state changes and emitted events. State changes are reported as net differences in native ETH balances and storage slots, alongside newly deployed contracts and their corresponding code hashes. If a specific storage slot is written to multiple times within a single transaction, it is reported as a single entry reflecting only its initial starting value and its final ending value. If a storage slot ultimately reverts to its original value by the end of execution, it is omitted entirely.
Three new EVM instructions provide programmatic access to this data. TXTRACE enumerates net state changes and events, TXDIFF retrieves starting and final values for specific addresses and storage slots, and EVENTDATACOPY copies event data directly into memory. These opcodes function exclusively within a POST_TX frame, executing as a static call at the conclusion of the transaction. This ensures that assertions can inspect the final outcome without altering the state themselves. If the defined rule is violated, the execution body reverts, yet the transaction remains recorded on-chain with a failed status, ensuring that the gas payer is properly charged for the consumed computational resources. This economic friction prevents malicious actors from spamming block builders with deliberately failing transactions for free.
The Assertion Has to Be Required
Because EIP-7906 does not inherently mandate that every transaction include an assertion, transaction builders retain the technical capability to omit them. Consequently, user-facing wallets must actively ensure that every frame transaction they construct incorporates the necessary assertion, derived either from local transaction simulations or standing user policies.
Similarly, protected protocol functions must cryptographically verify that incoming calls originate from frame transactions containing the exact required assertions. Contracts must reject standard transactions as well as frame transactions carrying missing or incorrect assertions. As a result, callers and integrations must adopt compatible frame transactions, noting that already deployed, immutable smart contracts cannot retroactively add this validation layer.
Where Transaction Assertions Could Help
Beyond immediate user and protocol security benefits, native transaction assertions could unlock advanced functionality across the broader ecosystem. They could significantly strengthen cryptographic delegation models. When delegating operational authority to an automated agent, users could enforce strict limits on which contracts the agent interacts with, how much capital it can deploy, and how long its permissions remain active. Assertions would introduce programmatic constraints on the exact economic outcome of every transaction executed by an agent.
Protocols could likewise define standardized safety rules enforced across all callers utilizing frame transactions. In solver-based execution architectures, a protocol could specify the required outcome while granting solvers the freedom to determine the optimal routing path. Such guarantees, however, would remain localized to a single transaction on a single network, excluding cross-chain routing workflows. Furthermore, assertions could verify that complex multi-step workflows successfully reach their intended final state, ensuring that unspent tokens are reliably returned to the user and residual token approvals are revoked.
Help Shape the Design
Development and research surrounding native transaction assertions remain active components of the Ethereum Foundation’s Trillion Dollar Security initiative. Researchers are actively seeking feedback from wallet developers, protocol engineers, and security teams interested in utilizing these upcoming capabilities. Stakeholders can connect with the research team via email or participate directly in the ongoing EIP-7906 discussion threads to help refine the design. Additional details regarding network risk controls and priority initiatives remain available through the broader Trillion Dollar Security initiative portal.

Comments (0)