


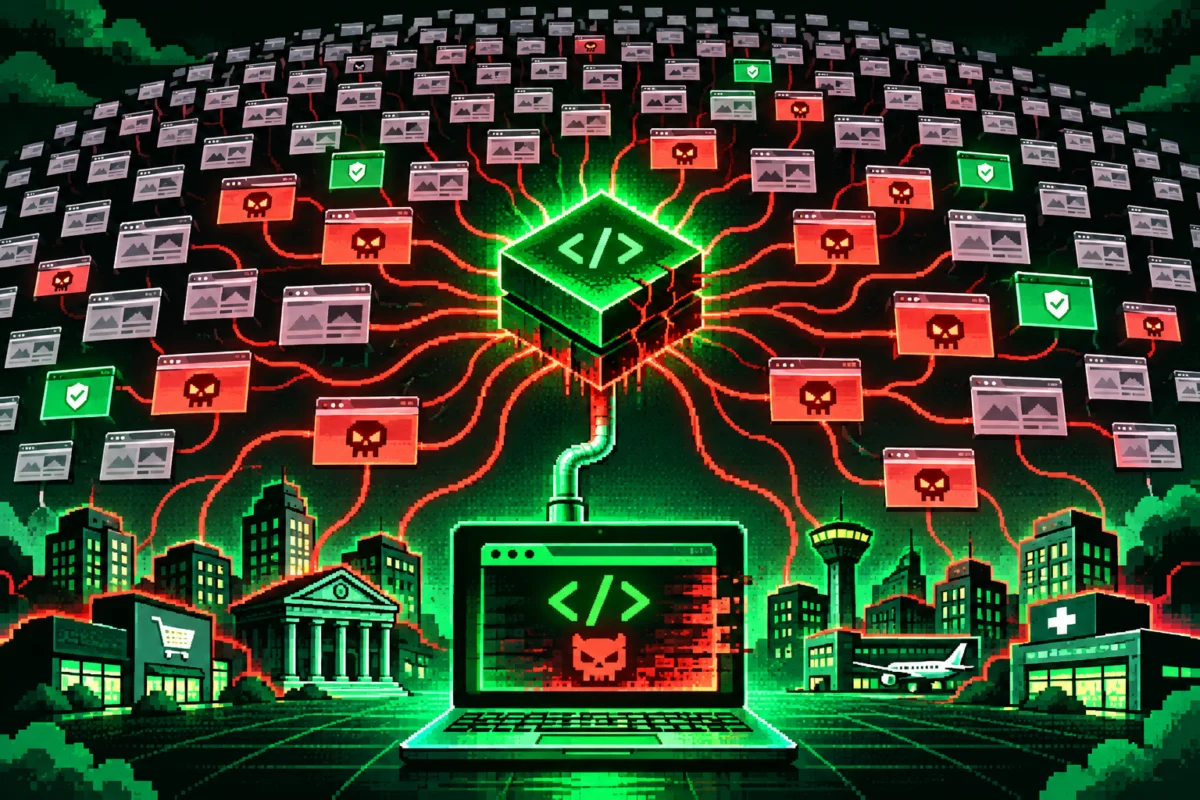
A widespread supply chain security incident originating from a vulnerability in the Optimizely Experimentation platform has compromised legitimate scripts deployed across prominent websites worldwide, raising urgent questions regarding third-party digital risk management, web application security, and the widespread absence of effective Content Security Policies.
The security event, which unfolded on November 16, involved threat actors leveraging a flaw within the Optimizely platform’s signup and project management flow. By exploiting this vulnerability, malicious actors were able to inject unauthorized JavaScript directly into customer projects. Because these projects were served through legitimate, trusted Optimizely snippets embedded in the codebases of prominent organizations, the malicious payload was distributed seamlessly to unsuspecting visitors across a wide array of high-profile web properties.
Independent investigations conducted by security researchers at Report URI, StepSecurity, Cynet, and BleepingComputer have shed light on the mechanics of the attack, which has been dubbed "OPTIMJACK." While the primary investigation cataloged an extensive inventory of potentially impacted domains—spanning 178 organizational entries across various global sectors—cybersecurity experts emphasize that presence in an inventory of hosted scripts does not automatically equate to confirmed network penetration of the host organizations themselves. Instead, the incident underscores the inherent risks associated with third-party client-side dependencies, where external scripts execute with the same privileges as native application code.
Mechanics of the Injected Malware
Technical analyses of the injected JavaScript payload revealed a multifaceted malicious architecture designed to extract value and sensitive data from end-users browser sessions. The attackers deployed several distinct functional modules within the compromised snippets.
One primary mechanism involved cryptocurrency address substitution, commonly referred to as a crypto clipper. The payload systematically monitored page content, clipboard interactions, and specific outgoing requests, altering valid cryptocurrency wallet addresses to divert funds to attacker-controlled destinations. Security researchers tracking the blockchain activity traced approximately $7,040 in receipts to identified wallets by the close of November 16, though analysts note that the total attributable financial loss remains uncertain and likely extends beyond early blockchain telemetry.
Simultaneously, the payload incorporated a card-skimming module activated at 13:43 UTC. This component was engineered to capture credit card numbers, expiration dates, and CVV codes entered into page-accessible forms by visitors. However, researchers observed that third-party, isolated payment iframes integrated into the affected sites were not directly accessible to the script due to cross-origin security boundaries.
In addition to financial theft, the malware included capabilities for browser data exfiltration. The script was capable of transmitting readable cookies and capturing screenshots associated with address substitution routines, though HttpOnly cookies remained protected and inaccessible. Furthermore, security telemetry indicated that on specific older versions of Apple’s iOS operating system, the injected code attempted to deliver Coruna and DarkSword exploit chains, though no confirmed metrics regarding successful mobile device compromises have been publicly established.
Industry Response and Corporate Statements
The public record following the incident reflects a complex landscape of vendor acknowledgments, corporate transparency, and third-party verifications. Optimizely publicly confirmed that an unauthorized party had exploited a vulnerability within its Experimentation platform, enabling the injection of malicious JavaScript into customer projects. The vendor stated that it swiftly remediated the vulnerability, removed the injected code, revoked compromised tokens, and reset access permissions. Furthermore, Optimizely indicated that it directly notified all affected business customers.
Major enterprises caught in the web of scrutiny have responded through varying channels. Zoom published a direct notice on its Security Bulletins page, acknowledging the Optimizely incident and confirming that, as a precautionary measure, it disabled Optimizely integrations across its production environments. Zoom’s advisory noted that initial internal reviews had not identified any adverse impact on customer data.
Other organizations addressed the incident through spokesperson statements provided to news agencies such as Reuters. Equifax stated that it had discontinued its use of Optimizely and found no evidence that its own systems were compromised. Similarly, home furnishings giant IKEA reported that it was actively assessing potential effects on its digital services and customers. Salesforce issued a dedicated trust advisory acknowledging unauthorized changes to Optimizely scripts on specific Salesforce-branded sites, confirming the immediate deactivation of those scripts and outlining conditional notification language contingent upon any identified unauthorized access to customer data.
However, security analysts caution that these public statements and media responses represent company acknowledgments rather than proof that every individual website visitor was directly notified. A distinct legal and operational gap remains between a vendor notifying its corporate clients and those corporate clients notifying millions of anonymous web traffic visitors.
Unanswered Questions and the Accountability Register
The incident has intensified industry discussions surrounding web application hardening, particularly the widespread failure of organizations to implement robust Content Security Policies. A CSP acts as a critical defense-in-depth mechanism, restricting the domains from which scripts can be loaded and executed, thereby mitigating the impact of third-party supply chain compromises. The relative ease with which the injected scripts executed across major media, financial, and technology portals highlights lingering gaps in client-side security monitoring.
As the security community continues to audit the scope of the event, researchers emphasize the necessity of distinguishing between different tiers of evidence. Official first-party security advisories, verified social media communications, on-record journalistic statements, and third-party technical scans represent distinct evidentiary categories. The 178 organizations initially cataloged in security inventories—spanning banking, technology, retail, media, travel, and healthcare—serve as an indicator of script exposure rather than a verified count of finalized customer notifications or compromised endpoints.
With remediation efforts largely completed by affected vendors and hosts disabling compromised snippets, the incident stands as a stark reminder of the systemic vulnerabilities inherent in modern digital supply chains, where a single point of failure in a marketing or experimentation platform can instantaneously ripple across the world’s most prominent digital properties.

Comments (0)