


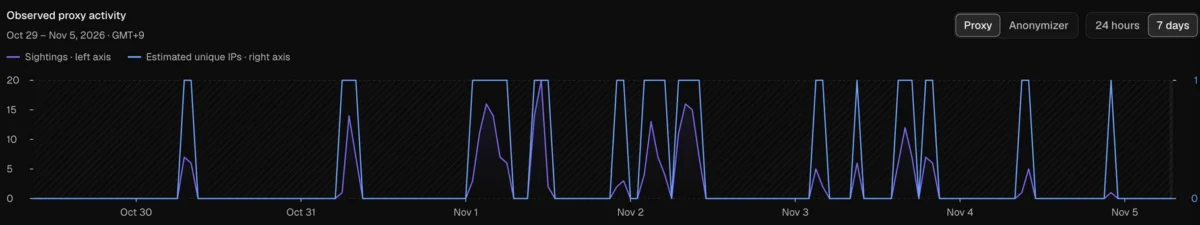
According to findings released by security firm Layer3 Intel, multiple residential proxy nodes were detected actively beaconing out from the dedicated internet address network reserved for the Executive Office of the President, identified formally as AS2650. Layer3 reported that this proxy activity maintained a relatively persistent presence between October 5 and November 3. A comprehensive review of the proxies available through AS2650 revealed that they successfully exited from the heavily guarded White House network 236 times during that roughly month-long window.
Further compounding the gravity of the discovery, the proxy tracking firm Synthient revealed via social media that the activity originating from AS2650 was directly tied to multiple Windows 11 installations running a service called Infatica. Infatica is a commercial proxy program frequently integrated into seemingly benign "free" mobile and desktop applications. The corporate lineage of the software adds an immediate layer of geopolitical and historical concern. Infatica was founded by Vladimir Fomenko, a Russian national whose previous web hosting firm, King Servers, served as ground zero for cyberattacks against state election systems in Arizona and Illinois back in 2016. At that time, King Servers hosted six of the eight specific internet addresses utilized by Russian state security services to compromise vital databases belonging to those state election systems.
The underlying mechanics of these networks present a constant security headache for defenders. There are currently dozens of residential proxy providers operating globally with varying degrees of legitimacy, a significant portion of which are based in countries like China or Russia. While their business models differ, their core function remains identical: they make it remarkably simple for paying customers to rent an unsuspecting third party’s residential or corporate internet address. This allows the renter to completely anonymize their web traffic or spoof their true geographic location. From the perspective of any website visited through these services, the incoming traffic appears to originate from the rented IP address rather than from the actual proxy customer operating behind the scenes.
Layer3 Intel’s detailed telemetry indicated that the unauthorized proxy exit nodes operating out of the White House traced back to six distinct internet addresses. This activity was registered on 26 out of 30 observed days, with the vast majority of the connections clustering during the evening hours, specifically between 5 p.m. and midnight, when normal office activity typically winds down.
Even more concerning to cybersecurity professionals, Infatica was far from the only service capable of channeling traffic through the inner sanctum of the American executive branch. Layer3 Intel disclosed that its investigation actually uncovered 28 separate residential proxy services that were somehow able to route their traffic and exit through this specific government network.
"This is public access," the Layer3 Intel research team wrote in a detailed analysis of the incident. "Anybody can obtain it by signing up to a public residential proxy service, paying a few dollars and sending requests through it. We did not selectively target this network or try to make our probes exit from it. We caught this by chance, simply by requesting global rotating access through these services."
As of publication, the White House has not responded to repeated requests for comment regarding how these services managed to infiltrate its secure network infrastructure.
The presence of residential proxies on government networks highlights a broader, systemic digital security crisis. As detailed in numerous cybersecurity reports over the past year, residential proxy services have quickly evolved into a major source of unwanted and frequently malicious internet traffic. Cybercriminals routinely exploit these networks to facilitate account takeovers, execute complex advertising fraud, and engage in mass content scraping to fuel resource-intensive artificial intelligence training projects.
Beyond mere nuisance traffic, these services introduce severe, structural security risks to any organization they touch. In late 2025, security researchers discovered that malicious actors were aggressively exploiting a widespread vulnerability inherent to many proxy networks. This flaw allowed unauthorized individuals to probe each individual proxy endpoint’s local network, searching eagerly for vulnerable systems to compromise and infect with malware.
The threat was underscored in January 2026, when dozens of commercial proxy services were forced to scramble and patch their networks. That emergency remediation came after Synthient Founder Ben Brundage publicly demonstrated how cybercriminals were actively abusing vulnerabilities in residential proxy services to seize complete control over devices residing inside the local networks of entirely unsuspecting users.
"Some of these resellers sell bandwidth for as low as 60 cents a Gigabyte, that means for less than a dollar you can gain access into some of the most confidential and trusted networks," Brundage explained in an interview. "The reseller ecosystem further enables this with any criminal able to buy access while skipping KYC [Know Your Customer] processes."
All too frequently, these dangerous proxy services make their way onto corporate and government networks through employee devices brought directly into the workplace. Software and app developers frequently monetize consumer applications by embedding software development kits provided by residential proxy networks into their code. This practice rewards the developer with a small financial payout for every single installation, effectively transforming user devices into silent proxy nodes without the owner fully realizing the implications.
Despite the obvious risks, these unauthorized proxy nodes are surprisingly common across high-value government and corporate environments. During an industry webinar held in January 2026, the proxy tracking service Spur revealed that it had detected residential proxies operating within nearly 300 government-owned and operated networks. The same tracking data found them inside 318 utility companies, 166 healthcare organizations and hospitals, and 141 financial and banking institutions. Furthermore, a security report published earlier this year by Infoblox noted that an astonishing 65 percent of its enterprise customer base had corporate networks querying one or more residential proxy-related domains, illustrating just how pervasive the invisible threat has become across modern digital infrastructure.

Comments (0)