


Every large enterprise now operates under an official mandate to integrate artificial intelligence into its core operations. Yet, despite widespread enthusiasm and heavy investment, very few organizations truly know what happens the exact moment an autonomous software agent is granted unrestricted access to enterprise systems and internal data repositories. Executives and security architects are left grappling with fundamental, high-stakes questions: What exactly will the agent be able to reach? How will the organization track and audit its actions? How can accountability be maintained across complex digital ecosystems?
According to industry observers and investors, these pressing concerns—rather than model quality, infrastructure costs, or a shortage of technical talent—are the primary reasons why so many enterprise AI programs remain perpetually stuck in early-stage pilot phases. Security teams want the productivity benefits of automation, but they fear the unmonitored blast radius of autonomous systems. This critical gap in the market is precisely what the cybersecurity startup Cymphony was built to address.
Agent Data Access is the Constraint
Across modern industries, employees are increasingly working hand-in-hand with AI agents to execute day-to-day business operations. However, the typical software agent bears little resemblance to a human employee. An autonomous agent can be provisioned and deployed in a matter of minutes rather than being recruited, vetted, and onboarded over the course of several weeks. It operates continuously without fatigue, and it can traverse far more systems, data silos, and operational capabilities than any individual human worker ever could.
Every single one of these unique properties is what makes an AI agent genuinely worth deploying in the first place. Simultaneously, however, every one of those exact same properties is what routinely forces corporate security teams to say no to deployment requests.
Governance and security are already proving to be major structural barriers to broader enterprise AI adoption. Recent industry projections from research firms like Gartner indicate that up to 40% of enterprises are expected to demote or decommission autonomous AI agents over mounting governance concerns by next year. This trend does not reflect a failure of underlying AI technology to perform its designated tasks. Instead, it highlights a profound organizational crisis: enterprises are being forced to pull back working, highly efficient agents simply because they lack the necessary visibility and control to see where those agents are roaming and what data they are accessing. The fundamental challenge facing modern businesses is not utility, but accountability.
For decades, enterprise security teams have built their operational tools around two distinctly separate pillars: determining where sensitive data actually lives, and strictly regulating who has access to it. The first pillar produced sophisticated data loss prevention tools designed to watch files, email inboxes, and corporate databases for unauthorized leaks. The second pillar gave rise to the massive modern identity and access management industry. However, both of these traditional paradigms were built upon a singular, foundational assumption: that the "who" accessing the system is always a human employee.
The rapid rise of AI has thoroughly broken that core assumption. A modern identity tool can tell an administrator that a specific agent exists within the network. A traditional data security tool can tell an organization that a particular file contains sensitive intellectual property or customer records. Crucially, however, neither tool can reliably tell you whether a given agent, acting on behalf of a specific human employee, possesses the capability to reach, modify, or exfiltrate that file right now. In the era of autonomous automation, identity security and data security can no longer be treated as separable domains.
Cymphony is the Solution
To bridge this dangerous security divide, Cymphony has developed a platform that continuously maps both human employees and autonomous agents across the entire enterprise ecosystem. The technology builds a dynamic, comprehensive graph illustrating precisely who and what can reach specific corporate systems and sensitive pieces of information.
Solving this challenge represents a notoriously difficult engineering problem. In a typical large enterprise, the exact same human user routinely holds a dozen different accounts scattered across legacy and modern systems that were never originally designed to communicate with one another. Furthermore, autonomous agents inherit their access permissions dynamically from the humans and applications that spawned them. Stitching all of these fragmented data points back together into a single, accurate, real-time picture requires far more than a basic dashboard that merely aggregates security alerts.
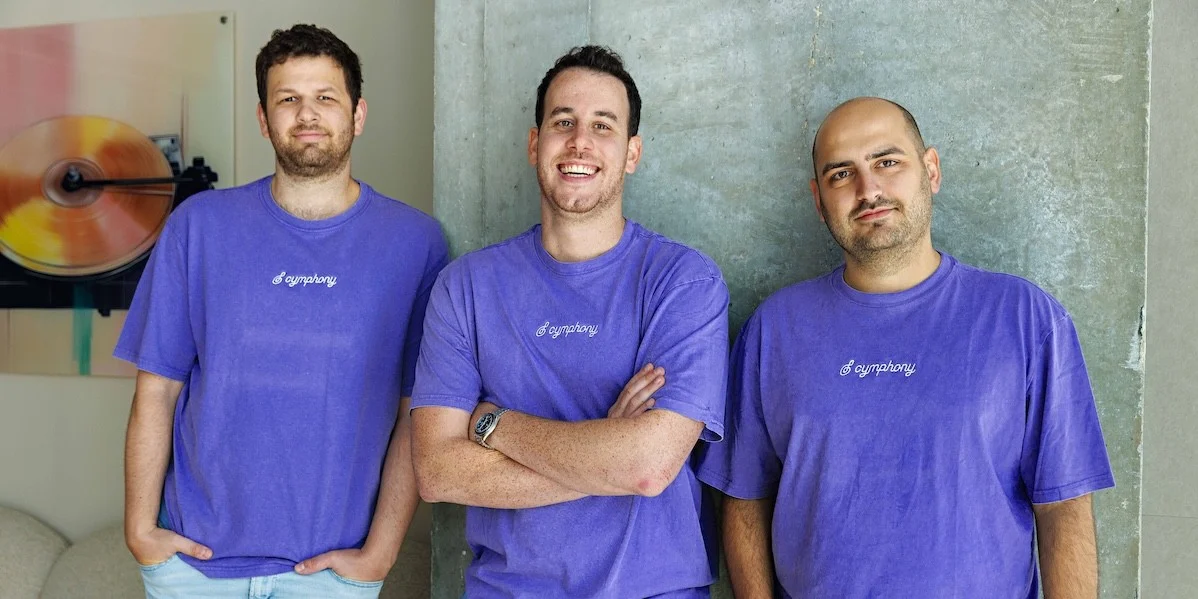
Industry partners and investors have taken note of the founding team’s pragmatic approach. The co-founders—Shy Dekel, Idan Berkovits, and Edi Gotlieb—possess a distinct instinct to build solutions not merely for the sake of generating alerts, but for embedding directly into existing enterprise workflows. Instead of stopping at threat detection and leaving a bewildered security analyst to figure out what to do next, Cymphony pushes the operational envelope further. The platform actively recommends and automates remediation steps, while seamlessly coordinating with the specific personnel who need to take swift corrective action.
Enterprise customers, including major global organizations such as Syngenta, KKR, Cass Information Systems, and Athennian, are already leveraging the platform and seeing tangible results. The momentum has also attracted significant financial backing. Sequoia Capital, which is also an active enterprise customer of the startup, initially led Cymphony’s seed funding round and has now returned to co-lead the company’s Series A financing.
Why We Partnered
The investors behind Cymphony’s latest funding round first connected with Shy Dekel, Idan Berkovits, and Edi Gotlieb through Sequoia’s extensive Israel network. They were introduced independently by two different contacts within their professional orbit, both of whom offered the exact same assessment: these three founders had spent their respective careers tackling difficult, unglamorous cybersecurity problems that most entrepreneurs actively avoid, and they were building something entirely unprecedented around that foundational expertise.
All three co-founders emerged from Israel’s elite Talpiot technological leadership program and possess deep, specialized experience in the national security and tech sectors. Shy Dekel previously led the cyber department for Unit 8200, Israel’s premier military intelligence agency. Idan Berkovits ran an advanced research group within the Office of the Prime Minister and was awarded the prestigious Israel Defense Prize. Edi Gotlieb spent years building complex hardware engineering systems at Apple and within the Israeli Ministry of Defense.
Historically, every major enterprise software category has been built upon a profound technological transition where the fundamental unit of work changes, rendering old security and management categories obsolete. The rise of cloud computing fundamentally altered where software ran, and the security industry completely rebuilt itself around that paradigm shift. The proliferation of mobile devices redefined what an endpoint was, and security adapted once again. In each historical instance, the companies that provided comprehensive visibility and precise control over the newly emergent operational landscape eventually became foundational infrastructure that everyone else took for granted.
Artificial intelligence represents the next great evolution in enterprise software, standing out as the very first technological shift where the new unit of work possesses the agency to act completely on its own. The company that successfully empowers an enterprise to say yes to autonomous agents—confidently, securely, at scale, and with a reliable audit trail of their actions—will not merely function as a temporary feature within the broader AI technology stack. It will serve as an absolute precondition for it. Cymphony is positioning itself to build that essential foundational layer, and its backers are betting heavily on its vision for the future of enterprise security.

Comments (0)