


Federal Bureau of Investigation agents have arrested a high-ranking executive at a Canadian cybersecurity firm in Pennsylvania, marking a significant escalation in the ongoing, high-stakes federal investigation into the notorious "ShinyHunters" hacking syndicate. According to multiple sources speaking with KrebsOnSecurity, the suspect was taken into custody following a sequence of events that has increasingly drawn scrutiny toward the shadowy intersection of corporate ransomware negotiation firms and elite cybercriminal enterprises.
The high-profile apprehension follows a public announcement and recent media coverage. The New York Times reported that federal authorities arrested a Canadian man in Pennsylvania on suspicion of providing illicit assistance to the ShinyHunters group, which recently breached the FBI to steal sensitive personal and professional data belonging to thousands of special agents. Neither the New York Times report nor a brief statement posted to social media by FBI Director Kash Patel identified the arrested individual by name.
However, sources close to the unfolding federal investigation revealed that the Canadian national was visiting Pennsylvania to attend a prominent cyber insurance conference. Investigators believe the suspect’s professional background—specifically within a specialized sector of the cybersecurity industry that handles ransomware negotiations and crisis advisory services with cybercrime groups—brought him into the crosshairs of federal prosecutors. Furthermore, sources indicated that operational control over the sprawling ShinyHunters investigation has now been officially centralized at an FBI field office in Texas.
An online review of industry events confirms that the Cyber Risk Summit was held at the Loews Philadelphia Hotel between October 5 and October 7. While the conference featured numerous sponsors and industry stakeholders, the summit’s official website identified its single largest sponsor as a Canadian security firm named Cypfer.
Public professional networking profiles on LinkedIn indicate that one of Cypfer’s prominent early figures was Edward Dubrovsky, who is currently associated with another Canadian security firm and conference sponsor known as CyberSteward. Approximately one month prior to his arrest, Dubrovsky published a post on LinkedIn announcing his explicit plans to attend the Cyber Risk Summit alongside members of the CyberSteward team, anticipating robust panel discussions and strategic networking sessions.

A spokesperson for Cypfer subsequently clarified that Dubrovsky was never a founder or co-founder of the enterprise, as his LinkedIn profile had claimed, but rather served as a managing director prior to his resignation in December 2025.
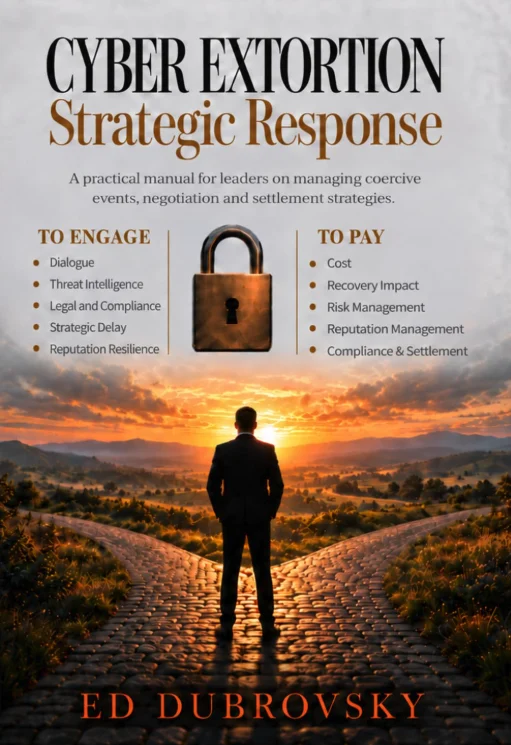
Before his departure from Cypfer and subsequent work with CyberSteward, Dubrovsky had established himself as a prominent voice in the specialized niche of cyber extortion defense. In a LinkedIn post leading up to the conference, Dubrovsky wrote that he was looking forward to continuing conversations around strategy and compliant-driven coercive ransomware advisory, negotiations, and global settlement services. He is also the author of a 252-page professional text titled Cyber Extortion Strategic Response, a manual that purports to guide corporate leadership beyond the initial ransom note and into the tactical decisions that dictate organizational recovery.
An excerpt from the book’s online distribution listing highlights a foundational premise taught within the industry: communicating with a digital extortionist is not identical to negotiating a payment, and entering into a negotiation does not constitute a commitment to pay. The text suggests that strategic engagement can serve alternative defensive objectives, such as testing the legitimacy of threat actor claims, gathering vital intelligence, creating valuable operational time, and preserving options while an enterprise evaluates its legal and operational next steps.
Federal court records indicate that on October 8, an individual named Edward Dobrovsky—noting a slight spelling variation in the court filings’ rendering of the surname—was formally arrested in Pennsylvania and slapped with severe federal charges, including cyber extortion and conspiracy. While a substantial portion of the underlying court documentation, including the primary criminal complaint, has been placed under seal by the court, a handful of essential documents remain accessible and have been indexed on legal databases such as CourtListener.
The indexed summary of the complaint charges the defendant with conspiracy to threaten to impair the confidentiality of information with the explicit intent to extort money, alongside charges of interference with commerce by threats.
Inmate records maintained by the U.S. Bureau of Prisons reflect that a 54-year-old Edward Dubrovsky was initially detained at a federal detention facility in Philadelphia. However, court docket entries reviewed on CourtListener include an administrative notice filed on October 9 ordering the immediate transfer of the case to the U.S. District Court for the Eastern District of Texas. Sources familiar with the matter emphasize that the Eastern District of Texas has effectively become the epicenter and clearinghouse for the federal government’s comprehensive prosecution of the ShinyHunters infrastructure. The FBI has consistently declined to comment on the specifics of the ongoing investigation.

Publicly available judicial dockets indicate that Dubrovsky has not yet retained private legal counsel, nor has the court formally appointed a public defender to represent him in the early stages of the federal proceedings.
The ShinyHunters cybercriminal group has earned international notoriety for deploying sophisticated social engineering, strategic phishing campaigns, and compromised credentials to breach cloud environments and siphon vast repositories of data from corporate accounts at major software-as-a-service providers. Once the data is exfiltrated, the group routinely threatens to leak proprietary corporate files, source code, and user databases onto underground forums and extortion portals unless massive cryptocurrency ransom demands are satisfied. According to internal estimates and federal tracking, the syndicate has successfully extorted more than $70 million from corporate and organizational victims globally over the course of the year.
The arrest of the Canadian executive is just the latest domino to fall in an aggressive, multi-jurisdictional law enforcement crackdown against the collective. Sources indicate that federal investigators have spent weeks poring over digital devices and forensic media seized last month when law enforcement authorities in the Netherlands arrested Pepijn van der Stap, a reformed hacker suspected of playing a key role in the ShinyHunters conspiracy. With these evidentiary discoveries being analyzed, intelligence sources suggest that criminal charges against principals and operatives at other specialized ransomware negotiation and incident response firms may be imminent.
The pressure on federal law enforcement intensified dramatically in the wake of Van der Stap’s apprehension. An operative operating under the online pseudonym "Rey" promptly assumed leadership responsibilities within the fractured ShinyHunters organization. In an audacious display of defiance, Rey began publicly taunting the FBI on social media platforms over a devastating breach that compromised the bureau’s online recruitment portal. That specific intrusion exposed highly sensitive background details on thousands of job applicants and active agents, including organizational unit assignments, security specializations, and confidential medical and psychiatric records.
Law enforcement agencies moved swiftly to neutralize the new threat actor. International news reports detailed that the individual operating behind the handle Rey had been identified as a teenager named Saif Al-din Khader, who was subsequently detained and began cooperating with federal investigators. Reporting highlighted how Khader was tracked down as the cybercrime collective actively attempted to execute an extortion scheme against a digital aviation and navigation unit that had been divested by aerospace giant Boeing late last year.
As federal authorities continue to execute search warrants, analyze foreign intelligence, and untangle the complex web of facilitators operating on the fringes of the cybersecurity industry, the investigation remains exceptionally fluid. Additional developments and court disclosures are expected as the prosecution proceeds in federal court.

Comments (0)