


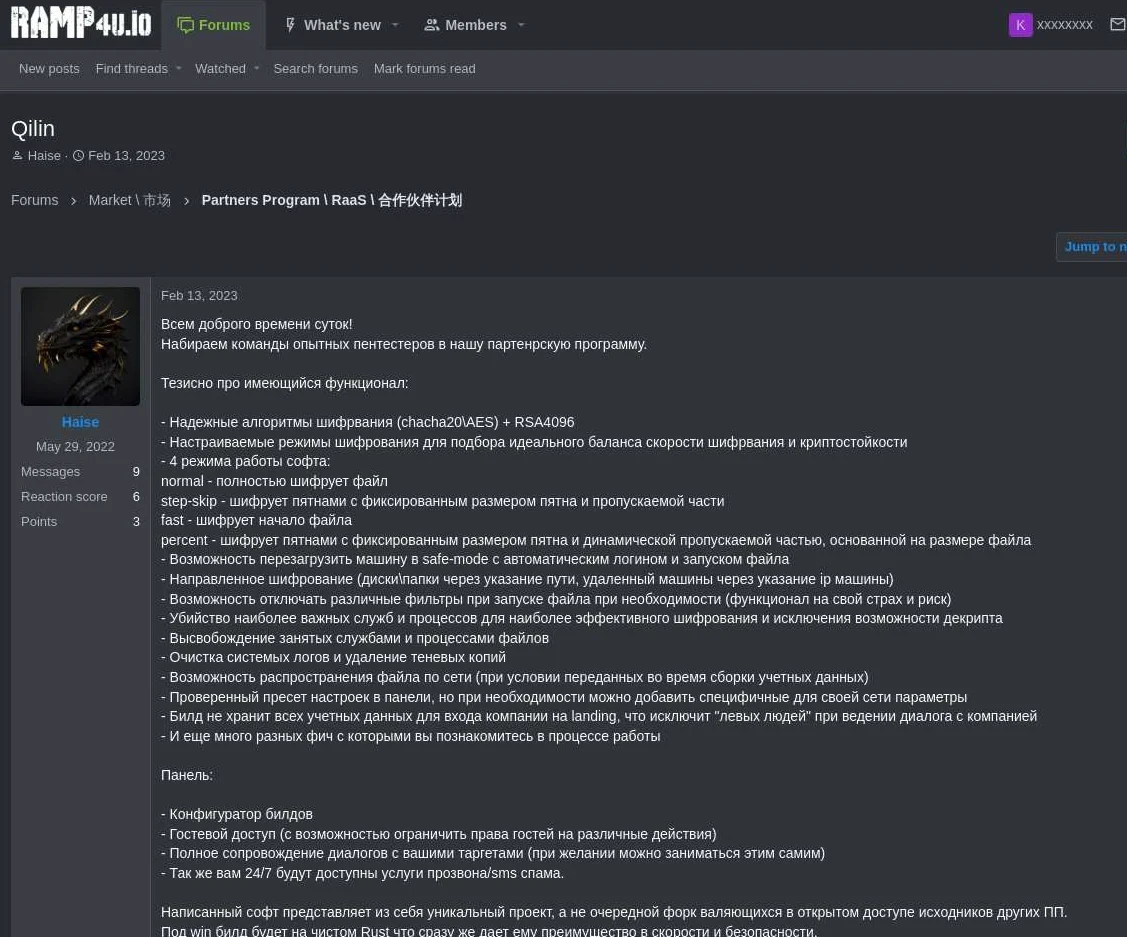
The cybercrime ecosystem has long relied on the illusion of impenetrable anonymity, yet even the most prolific threat actors eventually slip up. The notorious cybercrime collective known as Qilin has cemented its reputation as the world’s most active ransomware affiliate program, claiming at least 365 victim organizations over the span of just three months. Despite running a high-stakes, highly lucrative criminal enterprise, the central administrator steering Qilin has made a series of foundational operational security errors over the past decade. A comprehensive trail of digital breadcrumbs now points directly to a 36-year-old man residing in St. Petersburg, Russia.
Operating continuously since September 2022, the Russia-based syndicate has risen to the top of the ransomware-as-a-service (RaaS) landscape. According to a quarterly threat intelligence review published by cybersecurity firm NCC Group, Qilin currently stands as the most industrious operation of its kind in the global threat landscape. (For perspective, investigative reporting earlier in the year profiled the leadership behind competing groups like The Gentlemen, another prominent player in the extortion economy).
Qilin recruits skilled affiliates to breach corporate networks by offering them an exceptionally generous cut—at least 80 percent of any extortion payout extracted from victims. Like many modern enterprise threat groups, its members utilize a "double extortion" methodology: operatives quietly exfiltrate sensitive corporate data before deploying encryption lockouts across victim systems, subsequently threatening to leak the stolen proprietary files onto the public web if demands go unmet.
Unlike the insular traditions practiced by many Russian-speaking ransomware partnerships, Qilin actively welcomes English-speaking affiliates into its fold. The group’s leader has openly discussed these collaborations on Telegram, noting partnerships with high-profile entities such as Scattered Spider and RansomHub.
The primary coordinator running Qilin operates under the digital alias "Haise." However, experienced cybercriminals frequently cycle through monikers as a standard operational security measure to sever ties with older, potentially compromised identities. While altering handles helps distance a threat actor from past mistakes—such as mixing personal details with illicit operations—this strategy carries inherent risks. When applying for membership on new, heavily vetted criminal forums, operators are often required to reference their historical aliases to prove their background and trustworthiness. When those forums eventually suffer catastrophic security breaches or law enforcement seizures, those historical links become public.
That exact vulnerability proved fatal to Haise’s anonymity. According to records maintained by the cyber intelligence platform Intel 471, an operator using the Haise handle applied for membership in June 2022 to RAMP, a tightly guarded Russian cybercrime forum originally established as a dedicated sanctuary for ransomware affiliate programs. Archived direct messages from RAMP—which was ultimately seized by the FBI in January 2026—reveal that the forum’s administrator approved the application while explicitly tying the Haise handle to a specific Telegram username: Alexbigboss44.

Expanding the investigation through the Intel 471 platform shows that the Alexbigboss44 handle was actively utilized two years earlier, in 2020, by an actor operating under the username "Rjun" across prominent Russian cybercrime forums including Exploit and XSS. According to intelligence compiled by Flashpoint, another major threat intelligence provider, Alexbigboss44 maintained a prolific presence across various underground forums and Telegram channels. That activity centered heavily on the illicit trade of web traffic, stolen browser logs, and compromised corporate access credentials.
Flashpoint’s analysis indicates that this specific persona engaged in the high-volume acquisition of Facebook logs and Google Ads accounts to facilitate fraudulent advertising campaigns and online gambling schemes. In these roles, the individual functioned simultaneously as a broker and an operator, managing a network of lower-level traffickers and purchasing compromised data feeds to fuel illicit monetization pipelines.
The definitive bridge connecting the Qilin administrator Haise to the older Rjun and Alexbigboss44 profiles was assembled and shared privately by IntelHawk, an artificial intelligence-driven platform specializing in de-anonymizing threat actors through historical username correlation, stylometry analysis, and behavioral signaling.
According to IntelHawk Founder and Chief Technology Officer Leo Bogod, a granular linguistic and historical analysis of these identities reveals a clear trajectory of criminal evolution. The individual progressed from a relatively novice web traffic arbitrageur and credit card fraudster between 2018 and 2019 into a sophisticated organizer of complex cybercriminal infrastructure between 2020 and 2023, shifting focus toward malware distribution, botnet management, and resilient payment systems.
Tracing these digital threads further yields profound operational overlaps. Intel 471 records indicate that by the time Alexbigboss44 submitted an application to the RAMP forum, the Rjun persona was already a long-standing participant across several other legacy Russian cybercrime boards, including Darkmarket, Verified, and Zloy. Registration logs show that Rjun consistently signed up for these platforms using a specific email address: [email protected].
Identity threat protection firm SpyCloud subsequently identified that this exact email address historically utilized the password "Rjun132." Pivoting that email address through Constella Intelligence, a breach-tracking service, revealed that it appeared within institutional records maintained by gosuslugi.ru, the official digital portal for state and municipal public services in the Russian Federation.
That specific government portal suffered a massive data breach in late 2025, which reportedly leaked more than 20 million citizen records containing full legal names, dates of birth, and primary mobile numbers. According to those leaked Gosuslugi files, the email address [email protected] officially belongs to a 36-year-old resident of St. Petersburg, Russia, named Aleksey Mikhailovich Yakovtsev.

Corroborating data from Flashpoint establishes that the Haise persona has long operated a specific Telegram account designated by internal user ID 118329521, logging more than 5,000 individual messages originating from the account since 2018. Educational registry data obtained from Russia’s federal education watchdog, Rosobrnadzor, indicates that Mr. Yakovtsev completed his primary grade schooling in Murmansk and later earned a master’s degree in computing and information systems.
Additional database queries run on that same Telegram user ID within Constella Intelligence link the account directly to the Russian mobile phone number +79602347275. Pivoting on that telephone number reveals further connections to auxiliary email addresses, including [email protected] and [email protected]. Furthermore, IntelHawk’s analysis shows that the telephone number is officially registered to Yakovtsev’s biological sister, and that Aleksey frequently utilized his sister’s email address when registering accounts across various commercial websites.
The mobile number also surfaces within historical airline flight manifests gathered from Russian travel agencies that experienced corporate data breaches in recent years. Those passenger manifests confirm that Aleksey Yakovtsev, born August 18, 1990, completed commercial flights between St. Petersburg and Murmansk on at least three occasions between 2013 and 2014.
More recent travel manifests indicate that while Mr. Yakovtsev has maintained no recorded international commercial flights outside of Russia, he frequently travels domestically between St. Petersburg and Sochi. Frequently referred to as the "Russian Riviera," Sochi is the nation’s premier resort city situated along the Black Sea coastline, located roughly 1,200 miles south of St. Petersburg by air.
Attempts to reach Mr. Yakovtsev for comment via his associated email addresses and telephone numbers were unsuccessful.
Parallel investigations into the matter have yielded matching conclusions. "Gang Exposed," an anonymous intelligence-tracking account on social media with a proven track record of successfully de-anonymizing suspected ransomware operators, published an independent assessment reaching identical conclusions regarding Haise’s true identity, explicitly crediting IntelHawk’s analytical platform for helping connect the fragmented digital puzzle pieces.

Comments (0)