


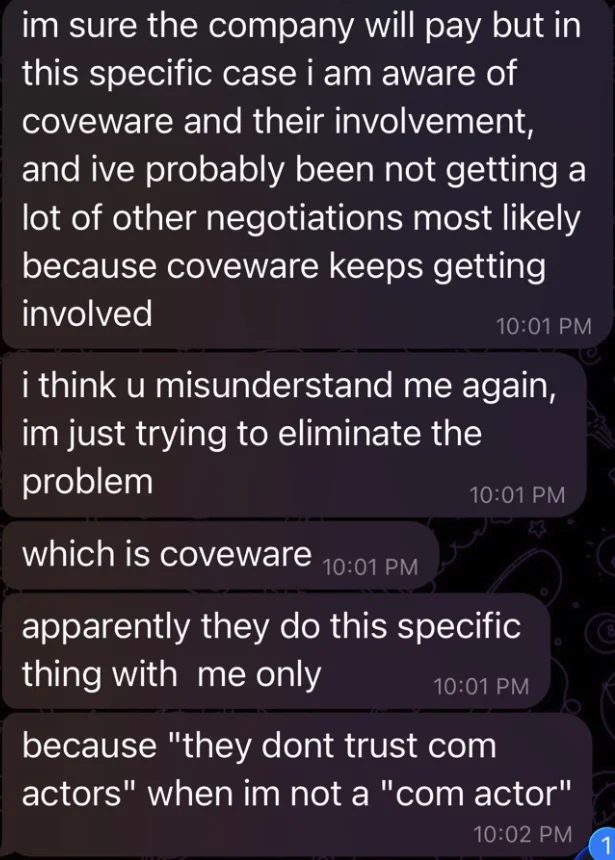
U.S. federal investigators pursuing the notorious ShinyHunters hacking group—which recently compromised highly sensitive data belonging to the Federal Bureau of Investigation—have uncovered alarming connections within the cyber-extortion ecosystem. According to sources close to the investigation, authorities have identified executives at two separate ransomware negotiation firms who maintained unusually close and illicit relationships with the extortion syndicate. In one particularly striking development, a U.S.-based executive allegedly helped ShinyHunters operate a dedicated pressure website designed to coerce victims into paying ransoms.
Hackers aligned with the ShinyHunters banner have claimed credit for dozens of major corporate and institutional data breaches since 2019. In its early days, the collective was primarily operated by cybercriminals residing in France. As those founding members were systematically arrested and jailed by international law enforcement, control of the ShinyHunters brand eventually shifted to an administrator known as "Rey." Last year, investigators identified Rey as a teenage hacker based in Amman, Jordan. According to official FBI estimates, the syndicate has successfully extorted more than $70 million from corporate and government victims over the course of the year.
The group’s operations crossed a critical threshold in late September, when hackers compromised the FBI recruitment website, fbijobs.gov. To mock the federal law enforcement agency, the attackers threatened to publish deeply sensitive stolen files. Reports indicate the compromised data included psychological and medical records, Social Security numbers, home addresses, and specific details regarding the professional specializations and units of FBI employees.
The brazen breach of its recruitment portal prompted the FBI to move with exceptional speed, detaining and questioning individuals who had maintained communication with Rey or other suspects associated with the syndicate. On October 3, Reuters reported that Rey had been detained by Jordanian authorities and was actively cooperating with federal investigators.

Rey’s rise to administrative control over the hacking group followed the sudden disruption of a senior associate. On the evening of September 15, law enforcement officers in the Netherlands executed a high-stakes arrest, apprehending convicted hacker and ShinyHunters suspect Pepijn van der Stap. Dutch tactical police reportedly deployed flash-bang grenades to stun Van der Stap and secure him while he was actively logged into multiple online accounts.
According to sources close to the probe, Dutch authorities apprehended Van der Stap while he was utilizing his Signal instant messaging application. This tactical timing allowed investigators to immediately review recent communications with frequent contacts, including ransomware negotiators operating out of Canada and the United States.
Multiple knowledgeable sources indicated that Van der Stap’s decrypted messaging logs provided the critical breakthrough needed to unravel a chilling murder-for-hire plot that surfaced immediately following his arrest. Dutch news outlet RTL reported last month that two foreign-targeted murders were allegedly planned, with indications pointing to Van der Stap as the individual who issued the orders, though law enforcement found no evidence that the plots were ever successfully executed.
The investigation quickly rippled across North America. On October 9, federal authorities arrested Edward Dubrovsky, a 54-year-old Canadian cybersecurity executive, in connection with the sprawling ShinyHunters probe. Dubrovsky had recently published a book on navigating cyber extortion that explicitly advocated for engaging with threat actors. According to federal court records, he was formally charged with threatening to disclose hacked or stolen data and interfering with interstate commerce through extortion. Politico reported that prosecutors requested Dubrovsky be held in custody pending trial, and that associated case records remain strictly under seal.
Insights shared by a source close to the investigation revealed that Van der Stap’s Signal archive demonstrated frequent, direct conversations between the Dutch hacker, Dubrovsky, and at least one executive at a prominent U.S.-based consulting firm. Troublingly, these executives often possessed detailed knowledge of fresh ShinyHunters victims before the victim organizations themselves were even aware they had been breached.

Furthermore, investigators uncovered potentially explosive evidence indicating that Dubrovsky knew ShinyHunters had successfully exfiltrated sensitive data from FBI servers. Despite this knowledge, he allegedly never notified the bureau prior to the syndicate publicly threatening on social media to publish the agency’s deeply personal personnel files.
SHINYWIRE
As the investigation deepened, federal agents uncovered evidence pointing toward active infrastructure support from the corporate sector. Investigators believe that at least one executive at a U.S.-based consulting firm played an active role in operating "shinywire[.]com," a now-defunct extortion portal utilized by ShinyHunters to pressure victims. While investigators have identified the firm—a prestigious organization with more than 1,000 associates—authorities have not yet publicly named the company or the suspected executive, as formal criminal charges have not been filed.
The Shinywire platform remained active from approximately May 3 until October 16, featuring profiles for nearly 100 organizations compromised by ShinyHunters. Each listing aggressively urged victim entities to engage with the cybercrime syndicate to negotiate payment terms. The pages featured samples of stolen proprietary data and warned that the complete caches would be leaked online if demands were ignored.
Cached records from monitoring services like urlscan.io captured extortion pages targeting organizations such as Intuitive Surgical, an American medical technology company breached in March after an employee fell victim to a targeted phishing email. Under the operational model of the site, victim organizations that refused to negotiate within a strict seven-day window found their stolen files published on the primary ShinyHunters shaming blog, which is accessible exclusively through the Tor anonymity network.
The fallout from these investigations has also exposed bitter corporate infighting. In mid-October, The Globe and Mail reported that in the months leading up to his arrest, Dubrovsky had filed a civil lawsuit in Ontario alleging he had become collateral damage in a campaign by a former business partner to destroy another industry leader.

Dubrovsky’s legal filings targeted Daniel Tobok, the former chief executive of Cypfer, a Toronto-founded cybersecurity firm with international offices spanning the United States, Britain, the Netherlands, the United Arab Emirates, and Mexico. Having launched Cypfer together after forming a partnership in 2017, the two executives suffered a bitter falling out by 2024, with Dubrovsky accusing Tobok of gradually freezing him out of business operations and making increasingly erratic decisions. Tobok denied the allegations, filing a counterclaim accusing Dubrovsky of misappropriating confidential information and engaging in unfair competition through a separate entity called CyberSteward Inc., while disputing Dubrovsky’s claim to founding status or equity share.
GHOSTBYTE
Interviews with former colleagues of Daniel Tobok revealed that years prior, he had been known to ransomware affiliates by the operational moniker "Ghostbyte." In 2018, a Canadian company targeted by Dharma—a prolific Russian-language ransomware affiliate program operational since 2016—reported that some encrypted files were permanently unrecoverable. While the victim leaned toward paying to recover operational capacity, they required guarantees that the extortionists would honor their word.
A redacted response from the Dharma representative directed the victim to an IT company in Canada capable of providing such guarantees, specifically recommending contact via the email address [email protected]. The representative advised the victim to establish a formal service contract, noting that payment would still be required.
While it remains unproven whether Tobok actively utilized the Ghostbyte email address, breach intelligence service Constella Intelligence identified that a primary personal email address frequently used by Tobok was associated with online accounts utilizing the "ghostbyte" username, including Snapchat. Furthermore, Constella traced the Dharma representative’s fallback email address to a cryptocurrency wallet that processed dozens of transactions totaling substantial sums.
In official statements issued in October, Cypfer maintained that its core business operations do not involve facilitating ransomware payments, noting that company leadership only learned of Dubrovsky’s arrest through media reports. The firm asserted it had received no outreach from law enforcement and was not the target of any ongoing investigation. Furthermore, Cypfer emphasized its independence from CyberSteward and noted its recent acquisition by the Apros Group, a holding company led by Jason Hogg, a former FBI special agent and former CEO of Aon Cyber Solutions Group. Aon previously acquired Cytelligence, a security consulting firm where Tobok served as founder and CEO and Dubrovsky acted as managing partner.

CONFLICTING INTERESTS
Under U.S. law, paying ransom to obtain decryption keys or secure promises to delete stolen files is not inherently illegal, provided the targeted group is not designated as a sanctioned entity by the U.S. Treasury Department. Because ShinyHunters currently lacks formal sanctions, corporate victims retain legal latitude to negotiate.
Organizations typically turn to specialized incident response firms under the direction of cyber insurance carriers. However, industry practices vary widely; while some firms operate on flat-rate retainers, others charge a percentage fee scaled to the total ransom paid. Security experts warn that percentage-based models create an inherent conflict of interest, incentivizing negotiators to push for higher payouts rather than aggressively driving down costs.
This dynamic has drawn intense scrutiny from federal prosecutors. In October, the Department of Justice charged MonsterCloud CEO Zohar Pinhasi with wire fraud and conspiracy for allegedly charging clients millions for remediation while secretly paying ransomware actors a fraction of the cost behind their backs. Similarly, in July, Florida ransomware negotiator Angelo Martino was sentenced to 70 months in prison for conspiring with the BlackCat/ALPHV syndicate to extract maximum payouts from corporate victims by leaking confidential negotiation strategies.
As law enforcement continues to dismantle the infrastructure surrounding groups like ShinyHunters, the intricate and often shadowy intersection between corporate incident response, ransomware negotiation, and cyber extortion continues to face unprecedented regulatory and legal exposure.

Comments (0)