


Authorities in the Netherlands have arrested a 24-year-old convicted cybercriminal on suspicion of aiding in massive data thefts and high-profile extortion schemes orchestrated by the prolific and aggressive hacker collective known as ShinyHunters. The high-stakes arrest has triggered a volatile reaction across the underground cybercrime ecosystem, with remaining ShinyHunters members dramatically escalating their operations in the days immediately following the detention. The group’s retaliatory wave has included stealing highly sensitive information from the Federal Bureau of Investigation (FBI) and turning its sights toward extorting the notorious Russian ransomware syndicate known as Cl0p.
According to three sources familiar with the matter, the Dutch man taken into custody by law enforcement this month is Pepijn van der Stap, a convicted cybercriminal originally from Almere and Lelystad in the Netherlands. Van der Stap was previously convicted in late 2023 for his involvement in a sweeping series of data thefts and digital extortions. At the time, prosecutors estimated that those illicit operations generated between €1.5 million and €2.7 million in illegal proceeds.
During his landmark trial in late 2023, van der Stap admitted to living a dual existence that mirrored the classic Dr. Jekyll and Mr. Hyde narrative. By night, he secretly operated under the hacker handle “Umbreon”—named after the dark-type Pokémon character—extorting corporate victims and leaking stolen data on English-language underground hacking forums, including the now-defunct RaidForums and Breached. By day, however, van der Stap maintained a respectable professional profile, working as a software engineer at Hadrian, an Amsterdam-based cybersecurity startup. He also volunteered his technical skills with the Dutch Institute for Vulnerability Disclosure (DIVD), a well-known nonprofit security research organization dedicated to finding and responsibly reporting software flaws.
Van der Stap fully confessed to his extensive data theft and extortion activities during court proceedings. Consequently, he was sentenced to four years in prison, with one year suspended. In a peculiar twist during his legal proceedings, van der Stap initially opted to remain in custody rather than return home, asserting that he could not find better treatment on the outside for his ongoing psychological challenges. He claimed these struggles included post-traumatic stress disorder stemming from childhood trauma. He was eventually released from prison in December 2025.
In an interview with KrebsOnSecurity on September 9, 2026, van der Stap cast himself as a thoroughly reformed hacker who was desperately trying to turn his life around and make a positive, constructive contribution to society. At the time of the interview, van der Stap was employed as an offensive security lead at Neo Security, a Dutch cybersecurity firm that has since declined to respond to repeated media requests for comment.
During the discussion, van der Stap noted that he was still actively dealing with civil lawsuits and financial restitution demands tied to his past cybercrime victims, insisting he was doing his absolute best to make amends. However, not long after that interview concluded, the Dutch hacker abruptly stopped replying to incoming messages. Efforts by associates and individuals close to him to establish contact repeatedly failed over the subsequent two weeks.
According to two sources with direct knowledge of the investigation, van der Stap was arrested by Dutch law enforcement on or around September 16 and has been held in custody for intensive questioning ever since. One source reported that a colleague personally witnessed Dutch authorities carting physical items and equipment out of van der Stap’s residence during the raid.

Law enforcement agencies in the Netherlands have faced mounting pressure in recent months and have actively appealed to the public for assistance. Earlier in September, police published a recording of a telephone call from February 2026, asking citizens to help identify the native Dutch-speaking voice of a ShinyHunters member who successfully social-engineered their way into Odido, the nation’s largest mobile telecommunications provider. During that Odido intrusion, attackers tricked an employee into logging into a spoofed website, leveraging that fraudulent access to steal personal data belonging to more than 6.2 million Dutch citizens.
Responding directly to Dutch news media outlets, ShinyHunters confirmed that the suspect heard in the police audio clip is indeed an active member of their collective. In a public statement shared with the NL Times, the group rallied behind their detained associate.
“Our team member has our full support—emotionally, mentally, and financially,” the hackers stated. “Everything has been arranged, including a criminal defense lawyer. We do not look down on our staff and members; we take excellent care of them.”
At the same time, the collective lashed out aggressively at Dutch law enforcement. “The Dutch police will need all the luck in the world—and everyone’s prayers—if they want to catch him before we carry out another large-scale data theft in the Netherlands,” the statement warned. “Frankly, the Dutch police are a big joke; they are incapable of doing anything. Incompetent. Irrelevant. Unimportant. Useless.”
FBI and Cl0p Hacks
Just days after sources confirmed van der Stap’s detention by Dutch authorities, ShinyHunters claimed responsibility for an unusually brazen and high-profile breach targeting the FBI’s job application portal at apply.fbijobs.gov. Reporting from 404 Media revealed that the data compromised in the incident included Social Security numbers and sensitive personal information belonging to more than 5,000 bureau officials.
Investigations by 404 Media and Reuters indicated that the pilfered FBI files contained specific job titles and unit assignments, including special agents, threat intake examiners, personnel within the major cybercrimes units, and investigators tracking foreign state-backed cyber threats. Furthermore, Reuters examined internal documents shared directly by the hackers, confirming that they included highly sensitive psychiatric and medical files belonging to FBI personnel. The bureau subsequently issued a brief public statement acknowledging the security compromise of the job portal.
According to ShinyHunters, access to the FBI portal and other victim networks was achieved by exploiting a recently patched vulnerability—tracked as CVE-2026-35273—in PeopleSoft, a widely used enterprise software-as-a-service platform owned by Oracle. The system is heavily relied upon by global organizations to manage human resources, hiring pipelines, employee benefits, and payroll functions. Oracle swiftly released a security update to remediate the PeopleSoft vulnerability after discovering that ShinyHunters had begun actively exploiting it as a zero-day flaw as early as June. Concurrently, Mandiant released specific web application firewall rules to protect organizations unable to immediately apply the official vendor patch.
However, security researchers reported that ShinyHunters bypassed Mandiant’s defensive mitigations by deploying a clever URL-encoding trick to circumvent the web application firewall rules. In a comprehensive threat intelligence report released on September 25, security experts at Mandiant and the Google Threat Intelligence Group confirmed that ShinyHunters had carried out a mass-exploitation campaign targeting the PeopleSoft vulnerability. This campaign compromised dozens of systems across diverse sectors, including higher education, technology, healthcare, agriculture, transportation, and government agencies.

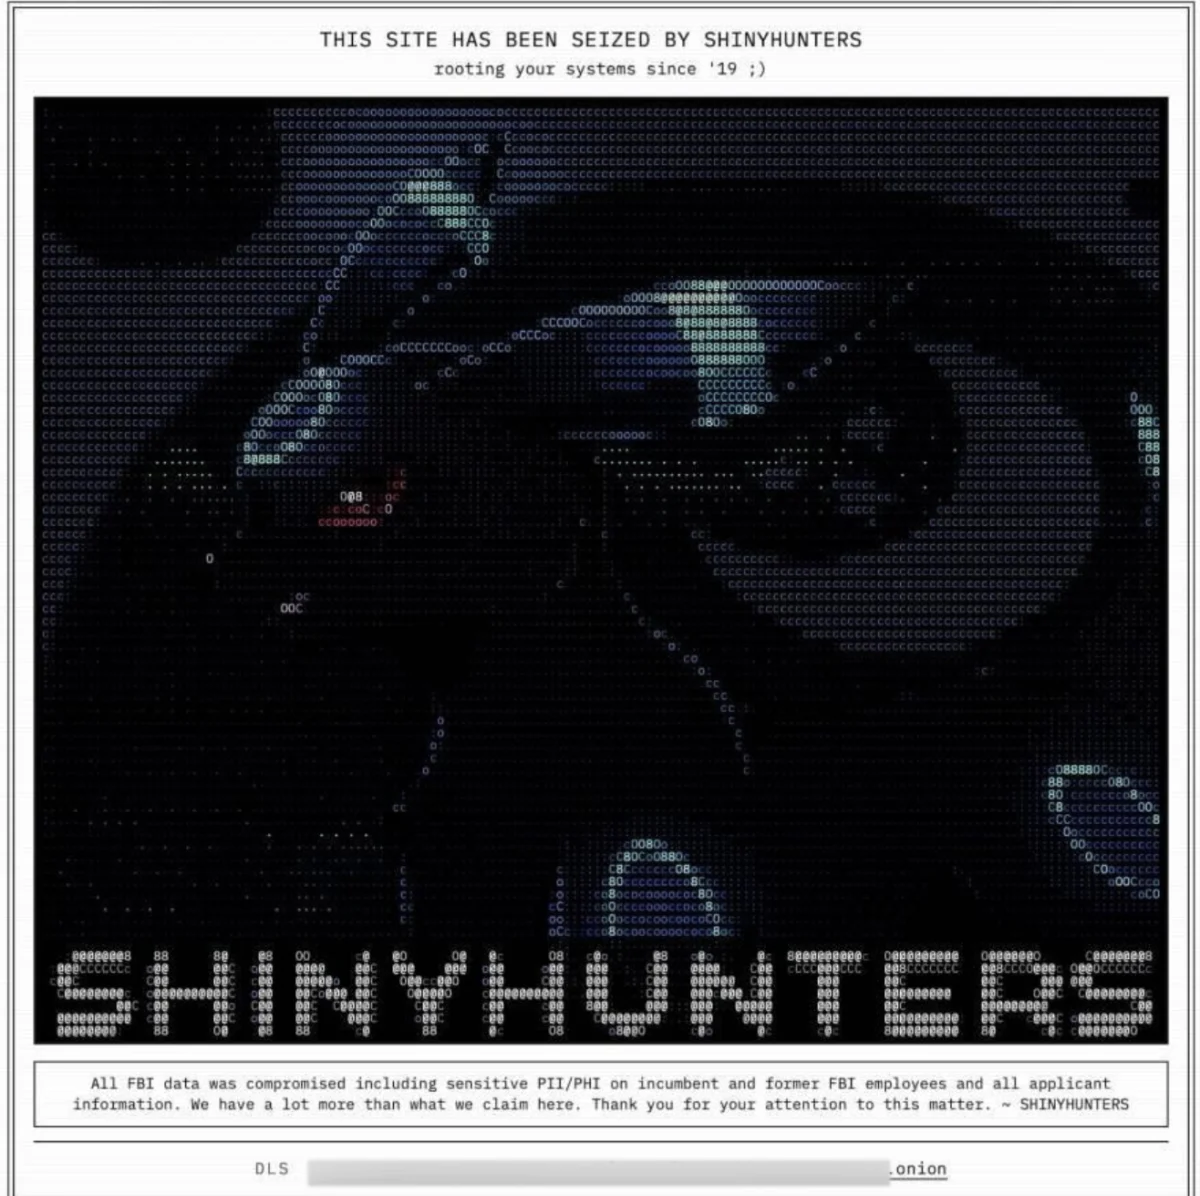
Intriguingly, van der Stap’s former hacker alias, Umbreon, appeared in plain sight within the imagery used by ShinyHunters to broadcast news of the FBI hack. The digital defacement message left behind on the compromised FBI jobs portal featured a detailed ASCII art rendering of the Pokémon character Umbreon alongside a taunting banner: “This site has been seized by ShinyHunters. rooting your systems since ’19 ;)” This exact visual style appeared identical to defacement imagery the group deployed during their 2020 hack of the English-language cybercrime forum Hackforums.
Multiple sources close to the unfolding ShinyHunters investigation noted that the group’s recent high-risk attacks against the FBI and a major Russian ransomware organization represent a sharp departure from the more measured operational style the gang previously favored. This sudden tactical pivot reportedly occurred after a leadership shakeup within the collective, which fell under the control of a teenage cybercriminal from Amman, Jordan. Operating under the online moniker “Rey,” the teenager is a prominent figure in an umbrella cybercrime syndicate known as ScatteredLapsussHunters (SLSH)—an amalgamation of three notorious hacking factions: Scattered Spider, LAPSUS$, and ShinyHunters.
Sources indicated that Rey held an ongoing personal dispute with the Dutch hacker regarding control over the ShinyHunters brand and its extensive stolen data repository. Consequently, cybersecurity analysts believe that prominently featuring the oversized Umbreon Pokémon imagery in the FBI job site defacement was a deliberate attempt by Rey to pin the high-profile attack directly on the imprisoned Dutchman.
Rey was first publicly unmasked by cybersecurity firm KELA in March 2025. Ahead of a subsequent security profile published later that year, researchers contacted Rey’s father to request an interview with his teenage son. Rather than intervening, the father forwarded the message directly to the teenager, who readily admitted to participating in past ransomware operations while claiming he was attempting to disengage from the SLSH network.
Blaming Umbreon
Immediately following widespread media coverage of the FBI job portal hack, Rey’s primary social media account on X began aggressively taunting both the Cl0p ransomware syndicate and federal law enforcement. One shared meme crudely depicted the groups as the New York twin towers being struck by aircraft labeled “cl0p drama” and “fbi breach claim,” with a giant float-sized figure of the Pokémon character Umbreon looming in the foreground of the city skyline.
Following further inquiries regarding Rey’s apparent rise to leadership within ShinyHunters, the teenager abruptly deleted his long-standing social media account. Meanwhile, Rey’s father, an employee of Royal Jordanian Airlines, failed to respond to numerous inquiries regarding his son’s alleged digital activities.
The underlying friction between SLSH and traditional ShinyHunters factions stems from a brief operational partnership earlier in the year. According to investigative reports published by Wired, the groups temporarily joined forces to better monetize valuable corporate credentials amassed by TeamPCP, an upstart gang that successfully compromised global code supply chains with malicious software but struggled to convert stolen data into financial profits. Two alleged leaders of TeamPCP were arrested in Australia, with one claiming their total earnings amounted to a mere $20,000.
Mandiant analysts later revealed that the security firm had successfully infiltrated TeamPCP and was secretly responsible for neutralizing the stolen credentials by rapidly feeding them to major cloud infrastructure providers like Amazon and Microsoft, which promptly invalidated the stolen keys. As the stolen access evaporated, the cooperating hacker factions quickly turned on one another, assigning blame for the burned credentials.

According to reports, ShinyHunters ultimately went rogue, executing independent extortion campaigns using TeamPCP credentials without sharing profits with the supply-chain hackers. Austin Larsen, a security researcher at Mandiant, noted that ShinyHunters has enjoyed a highly lucrative extortion spree throughout the year, putting the collective on track to amass nearly $100 million in illicit payouts by the end of 2026.
In contrast to financially driven syndicates, van der Stap previously maintained that money was never his primary motivator. Instead, his early cybercriminal endeavors were driven by an obsessive compulsion to curate the world’s most comprehensive collection of stolen databases. In a 2024 interview with Bloomberg, van der Stap described his workflow candidly.
“The hacking was very easy for me, and it wasn’t a compulsion,” he stated. “My habit was collecting. Collecting data, organizing data, downloading data, creating folders.”
Meanwhile, the Dutch Institute for Vulnerability Disclosure (DIVD), where van der Stap previously volunteered, disclosed an internal cybersecurity incident involving the suspected malicious use of artificial intelligence. While the nonprofit released limited details regarding the breach, a DIVD spokesperson confirmed to security researchers that the event appeared entirely unrelated to ShinyHunters and showed no ties to the past volunteer work of van der Stap.
Following the initial arrests, Dutch police officially confirmed the detention of a 24-year-old suspect tied to the ongoing ShinyHunters investigation. Authorities announced that the individual would appear before the chambers of the Rotterdam District Court to face formal proceedings.
Simultaneously, the FBI released a direct video message addressing the ongoing international crackdown on ShinyHunters. Brett Leatherman, assistant director of the FBI’s cyber division, thanked Dutch law enforcement partners for their critical assistance and issued a direct warning to remaining members of the hacking collective.
“Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left,” Leatherman said. “The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you. I suggest you reach out to us while the choice is still yours.”

Comments (0)